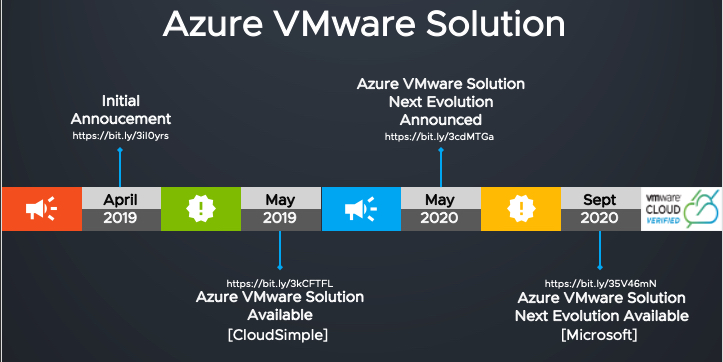
<?xml version="1.0" encoding="utf-8"?><feed xmlns="http://www.w3.org/2005/Atom" xml:lang="en"><generator uri="https://jekyllrb.com/" version="4.3.4">Jekyll</generator><link href="https://emadyounis.com/feed.xml" rel="self" type="application/atom+xml" /><link href="https://emadyounis.com/" rel="alternate" type="text/html" hreflang="en" /><updated>2026-03-28T21:47:41-07:00</updated><id>https://emadyounis.com/feed.xml</id><title type="html">emadyounis.com</title><subtitle>Deep dives on VMware, multi-cloud, workload mobility, and data center architecture — by Emad Younis, technologist with 20+ years of hands-on experience.</subtitle><entry><title type="html">Overview of Azure VMware Solution Next Evolution</title><link href="https://emadyounis.com/overview-of-azure-vmware-solution-next-evolution/" rel="alternate" type="text/html" title="Overview of Azure VMware Solution Next Evolution" /><published>2020-09-23T11:20:22-07:00</published><updated>2021-03-18T12:00:00-07:00</updated><id>https://emadyounis.com/overview-of-azure-vmware-solution-next-evolution</id><content type="html" xml:base="https://emadyounis.com/overview-of-azure-vmware-solution-next-evolution/"><![CDATA[<p><span data-preserver-spaces="true">The general availability (GA) for the next evolution of Azure VMware Solution (AVS) was announced <del>yesterday</del> during the <a href="https://news.microsoft.com/ignite-2020-book-of-news/#158-next-generation-azure-vmware-solution-now-generally-available">Microsoft Ignite 2020</a> virtual conference. This is a joint partnership between Microsoft and VMware, where Azure VMware Solution is a Microsoft managed service built on Azure bare metal infrastructure and cloud verified by VMware. The initial launch of the Azure VMware Solution in May of 2019 was by CloudSimple; this latest release is built and architected by Microsoft, providing an integrated experience with Azure services. Azure VMware Solution is currently available in the following 10 regions: East US, North Central US, West US, UK South, Japan East, West Europe, North Europe, Canada Central, Australia East, and Southeast Asia. More regions will be available in the future; additional details can be found by searching the </span><a href="https://azure.microsoft.com/en-us/global-infrastructure/services/?products=azure-vmware&amp;regions=all"><span data-preserver-spaces="true">Microsoft Products available by region page</span></a><span data-preserver-spaces="true">. Customers running the CloudSimple Azure VMware Solution version also have a </span><a href="https://docs.microsoft.com/en-us/azure/azure-vmware/faq"><span data-preserver-spaces="true">migration path to this latest release</span></a><span data-preserver-spaces="true">, leveraging VMware HCX.</span></p>

<p><img src="https://emadyounis.com/assets/img/2020/09/Azure-VMware-Solution-Releases.jpg?resize=723%2C362" alt="" /></p>

<p>Azure VMware Solution is powered by VMware Cloud Foundation: vCenter Server, vSphere, vSAN, and NSX-T. Also included is VMware HCX, the Swiss army knife of workload mobility. Customers can securely extend their networks and migrate workloads from on-premises (vSphere 6.x -7.x) to AVS or between AVS private clouds in different regions using a combination of migration options. Microsoft will handle the billing, lifecycle operations (upgrades), and troubleshooting of the service, allowing customers to focus on their workloads.</p>

<blockquote class="prompt-info">
  <p>Note: Updated 3/18/21 to include changes to the service.</p>
</blockquote>
<h2 id="getting-started">Getting Started</h2>

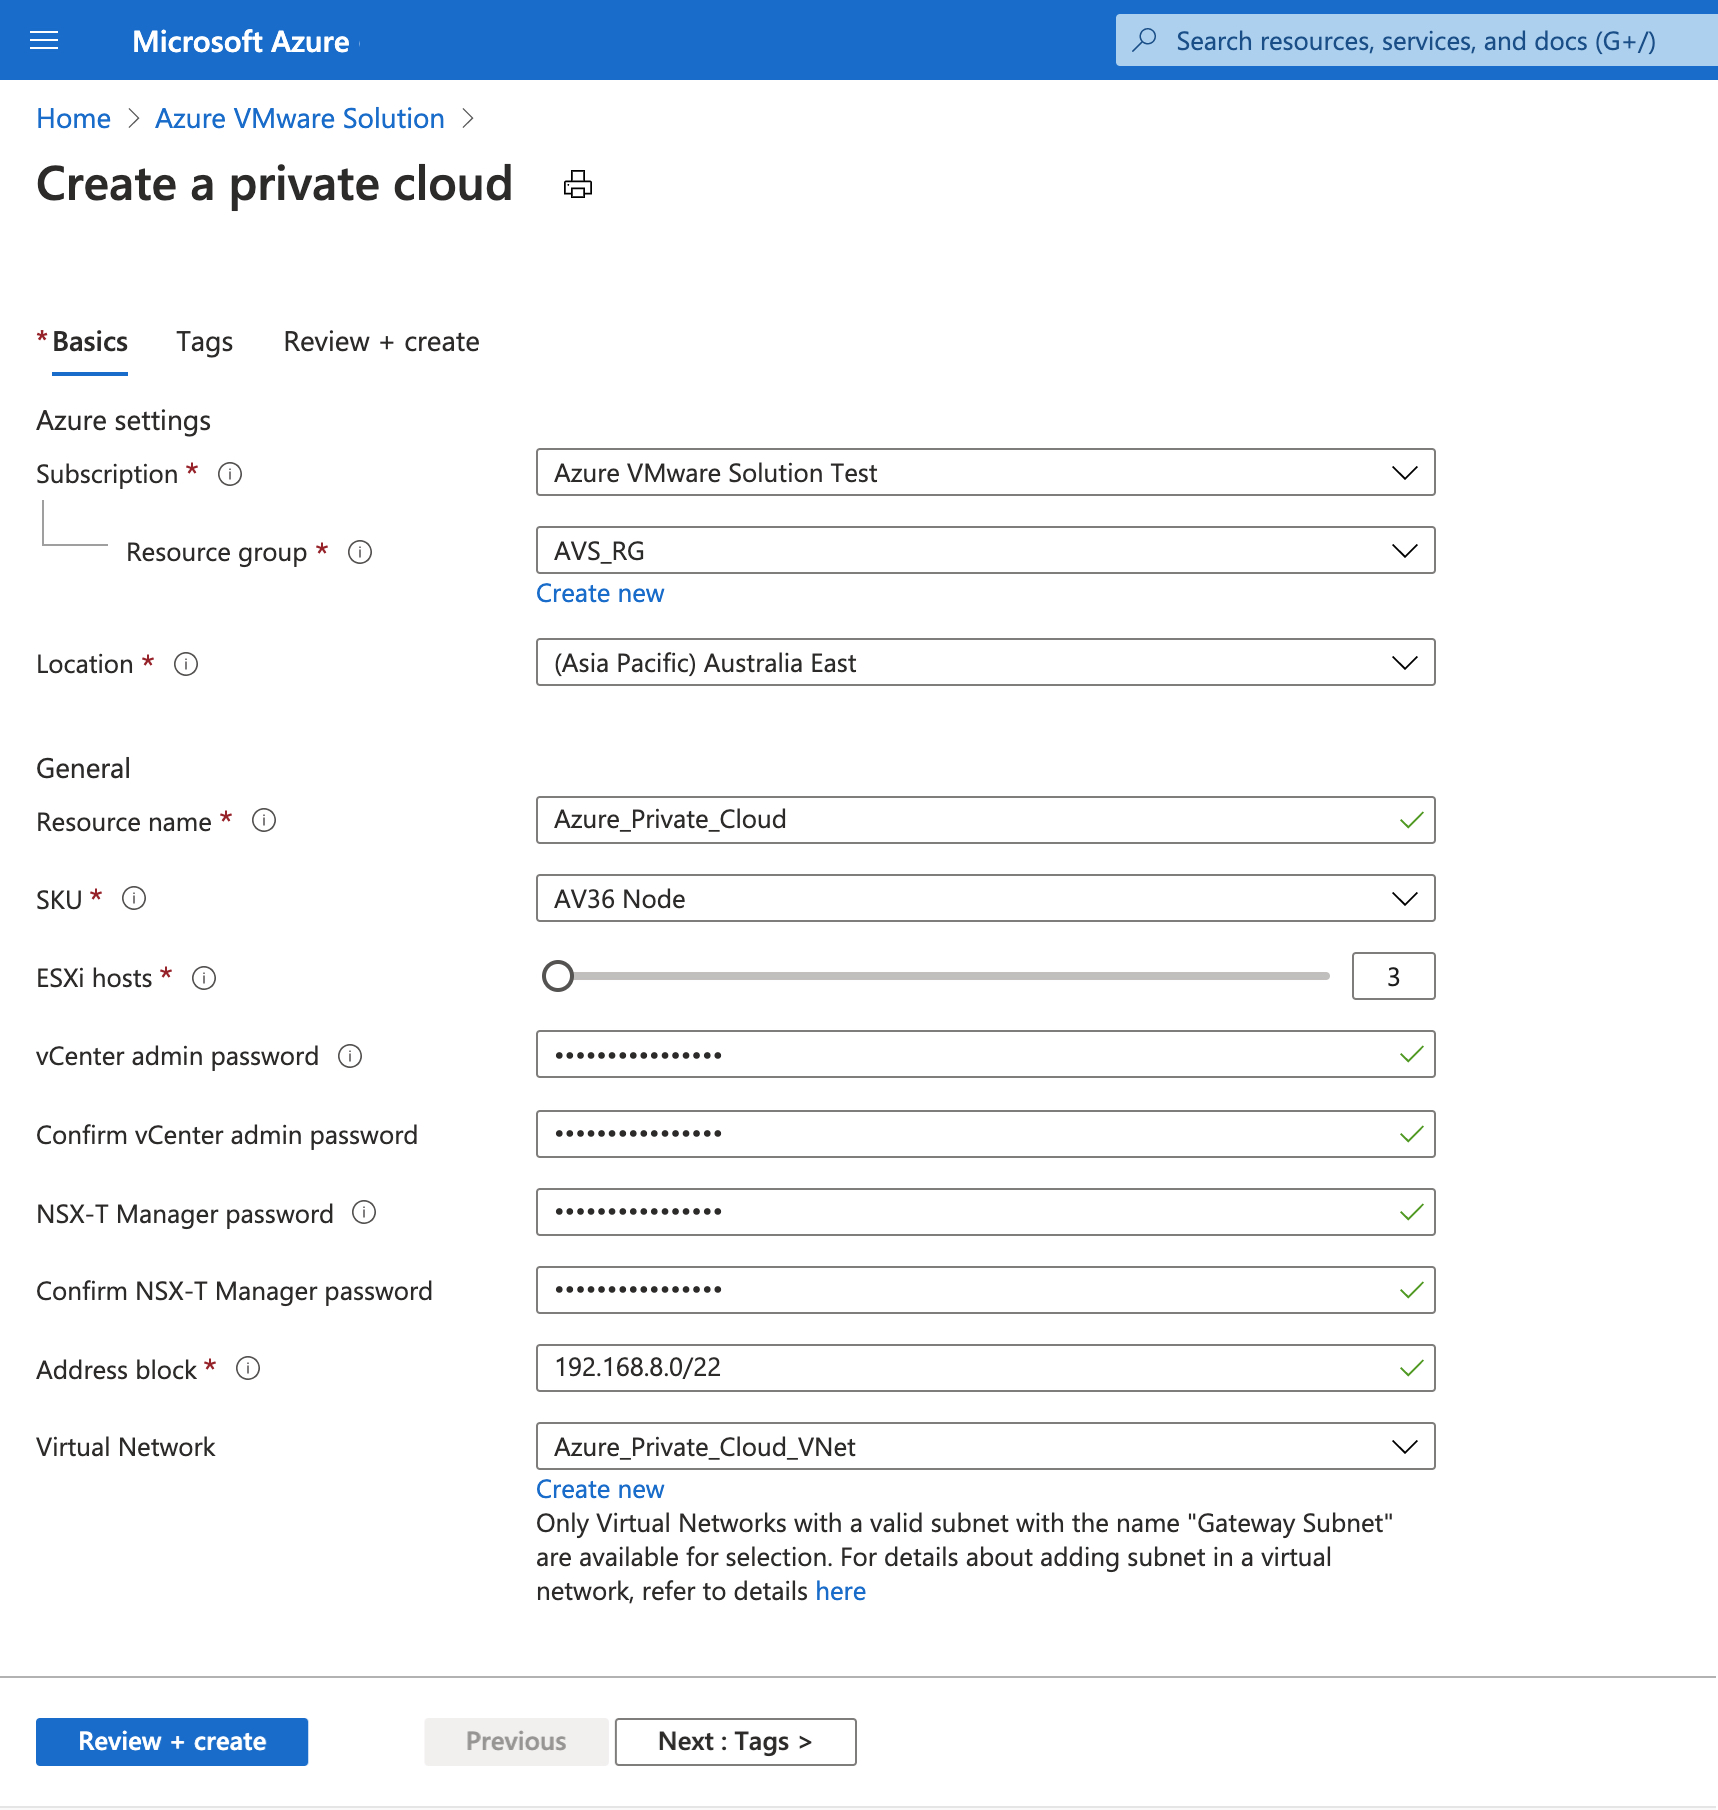
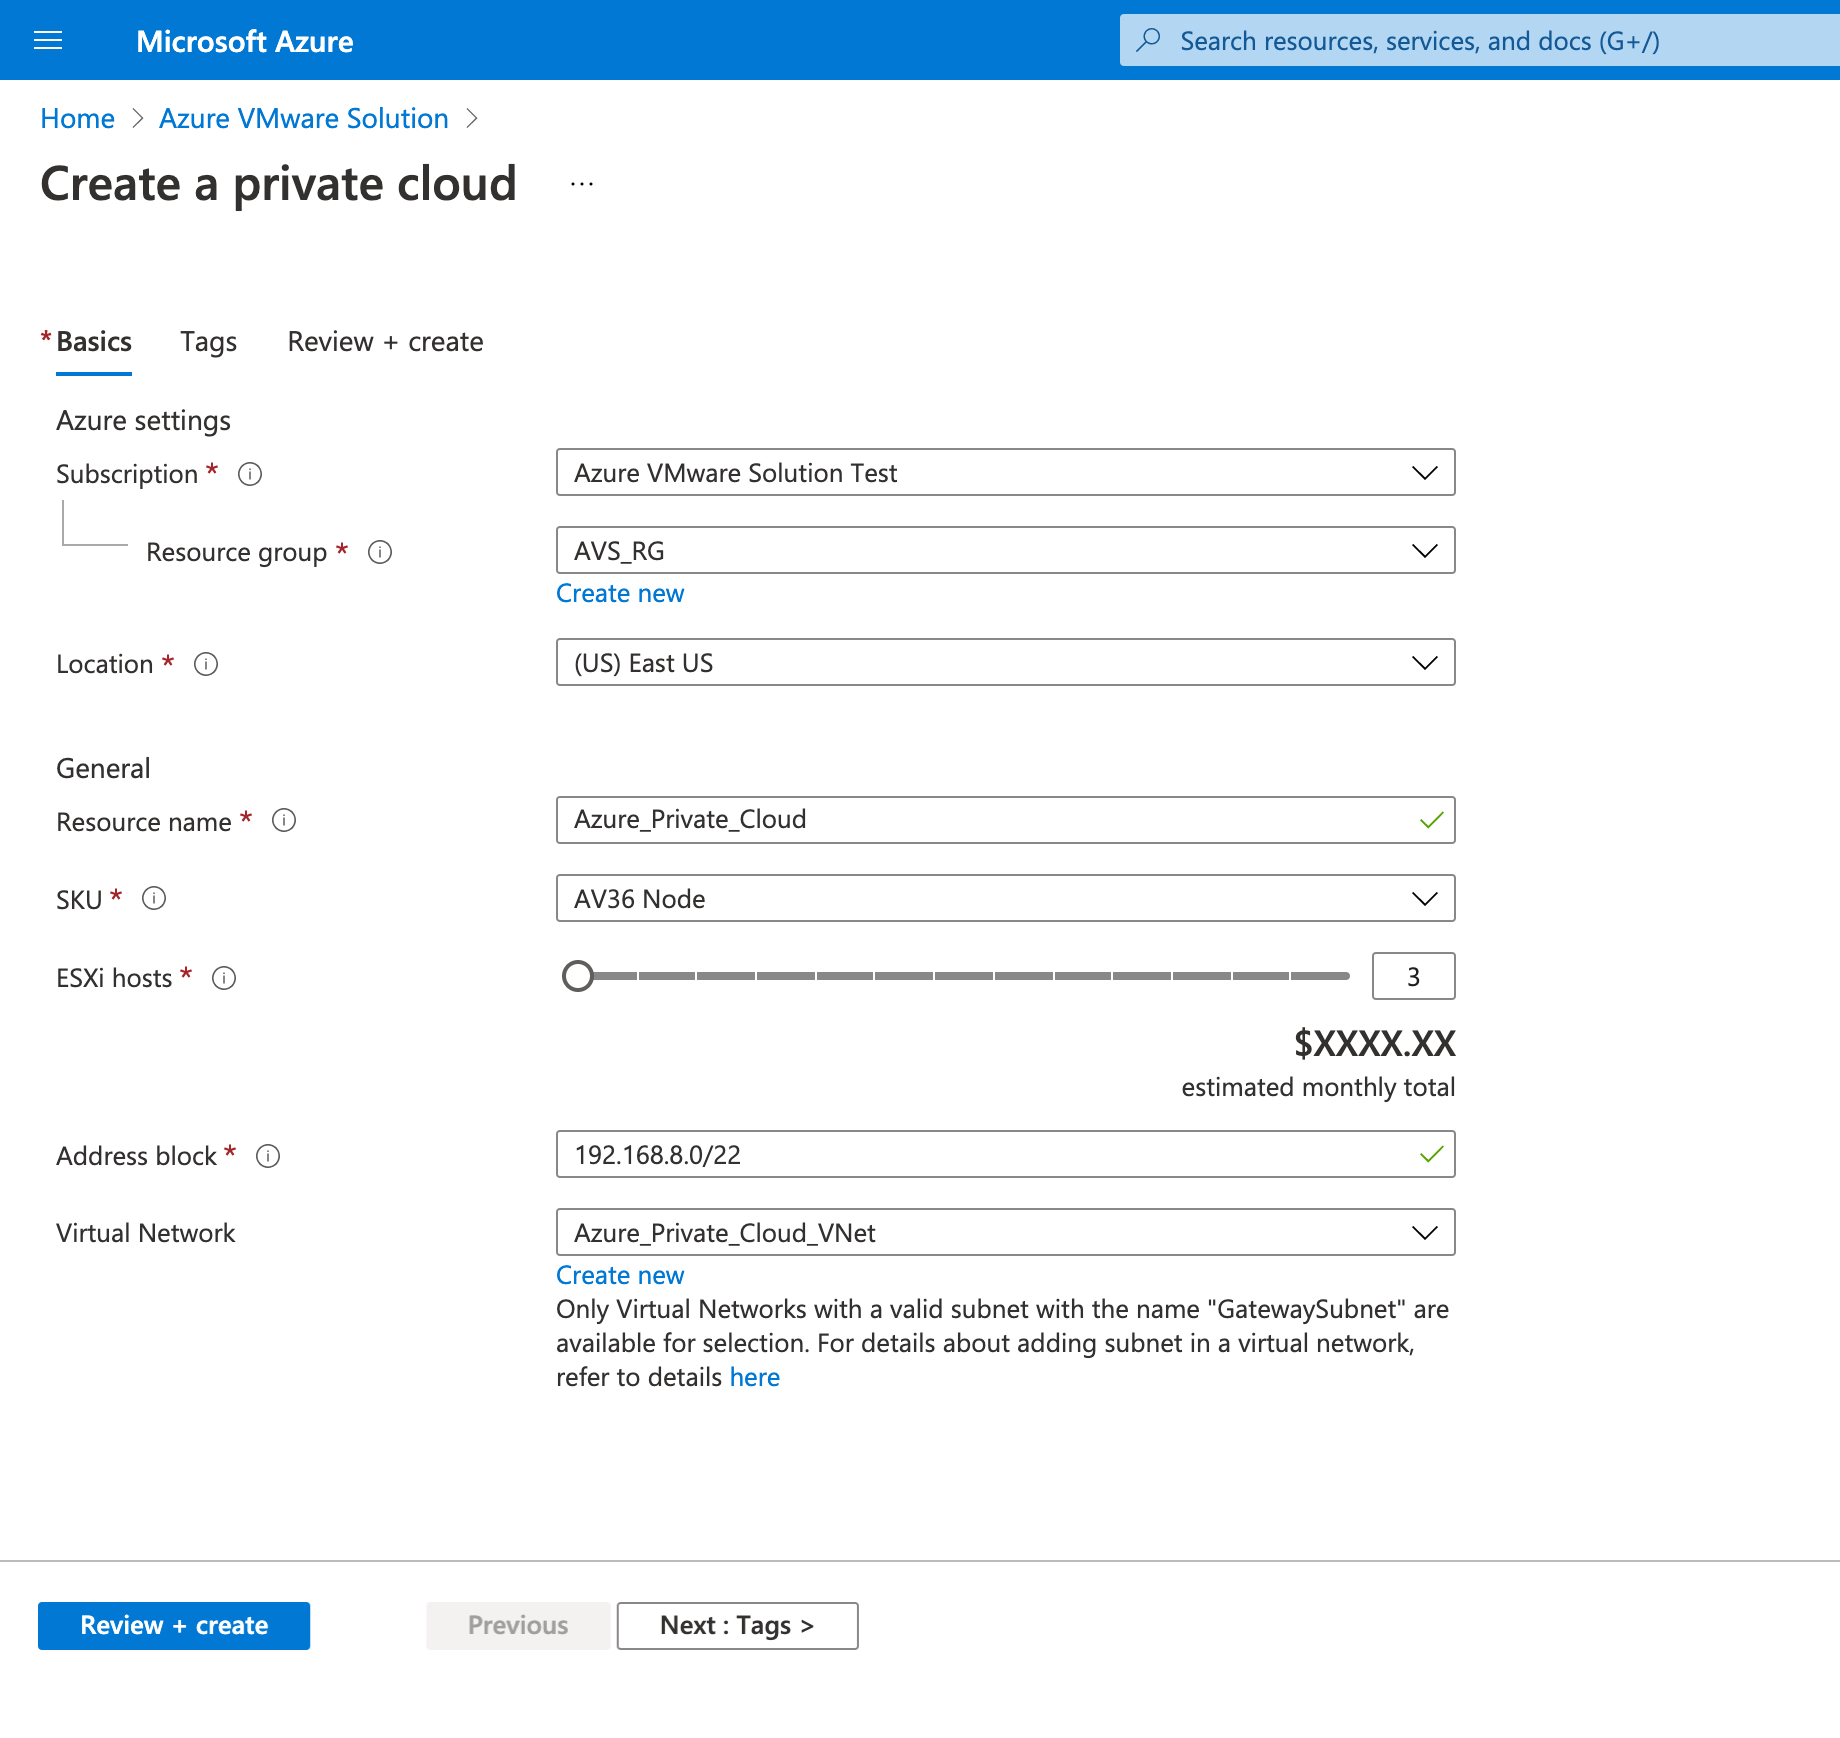
<p><span data-preserver-spaces="true">There are a few things you need to have in place before you can deploy an Azure VMware Solution private cloud. First, an </span><a href="https://azure.microsoft.com/en-us/free/"><span data-preserver-spaces="true">Azure account</span></a><span data-preserver-spaces="true">, which you can get for FREE. Next, your account must be associated with a </span><a href="https://docs.microsoft.com/en-us/azure/azure-vmware/enable-azure-vmware-solution#eligibility-criteria"><span data-preserver-spaces="true">subscription</span></a><span data-preserver-spaces="true"> that is either part of a Microsoft enterprise agreement or a Cloud Solution Provider (CSP). Finally, is requesting host quota for your subscription. Once quota is applied to a subscription, search for “Azure VMware Solution” in the Azure portal’s search box. Alright, you don’t need to type out the entire thing; it will appear within the first couple of characters in VMware. An option to deploy your first private cloud in your subscription will be displayed on the next screen. As part of the private cloud creation, there is some basic information needed:</span></p>

<ul>
  <li><strong><span data-preserver-spaces="true">Subscription </span></strong><span data-preserver-spaces="true">– Billing framework that provides entitlement to deploy and consume Azure resources</span></li>
  <li><strong><span data-preserver-spaces="true">Resource Group </span></strong><span data-preserver-spaces="true">– Logical way to group Azure services</span></li>
  <li><strong><span data-preserver-spaces="true">Location – </span></strong><span data-preserver-spaces="true">Where to deploy the private cloud</span></li>
  <li><strong><span data-preserver-spaces="true">Resource Name </span></strong><span data-preserver-spaces="true">– Name of your private cloud</span></li>
  <li><strong><span data-preserver-spaces="true">SKU </span></strong><span data-preserver-spaces="true">– Node type used during deployment</span></li>
  <li><span data-preserver-spaces="true"><strong>ESXi Hosts</strong> – Number of hosts to deploy, min of 3 by default with the option to increase to a max of 16 per cluster</span></li>
  <li><del><strong><span data-preserver-spaces="true">vCenter Admin Password </span></strong><span data-preserver-spaces="true">– password used to log in vCenter with cloudadmin@vsphere.local</span></del></li>
  <li><del><strong><span data-preserver-spaces="true">NSX-T Manager Password </span></strong><span data-preserver-spaces="true">– password used to log in NSX-T manager with admin </span></del></li>
  <li><strong><span data-preserver-spaces="true">Address Block </span></strong>– <span data-preserver-spaces="true">CIDR block used when deploying management components, requires a /22</span></li>
  <li><strong><span data-preserver-spaces="true">Virtual Network </span></strong><span data-preserver-spaces="true">– A representation of cloud networking and provides abstraction and logical isolation. An Azure environment can contain multiple VNets.</span></li>
</ul>

<blockquote class="prompt-info">
  <p>Note: Providing vCenter Server and NSX-T credentials during a private cloud deployment is no longer required, they are now auto generated. If they need to be rotated you will currently need to open a support request.</p>
</blockquote>

<p><strong>[Previous private cloud creation screen]</strong></p>

<p><img src="https://emadyounis.com/assets/img/2020/09/Create-Private-Cloud-Final-Image.jpg?resize=1718%2C1810" alt="" /></p>

<p><strong>[Updated private cloud creation screen]</strong></p>

<h2 id="private-cloud"><img src="https://emadyounis.com/assets/img/2020/09/Updated-AVS-Deployment.jpg?resize=1840%2C1738" alt="" />Private Cloud</h2>

<ul>
  <li>
    <p><strong><span data-preserver-spaces="true">ExpressRoute </span></strong><span data-preserver-spaces="true">– Is a private and secure connection from a customer’s physical datacenter providing dedicated bandwidth into Microsoft Azure. </span></p>
  </li>
  <li>
    <p><strong><span data-preserver-spaces="true">Global Reach </span></strong><span data-preserver-spaces="true">– Connects ExpressRoute bi-directionally from a customer’s environment to Azure VMware Solution. </span></p>
  </li>
</ul>

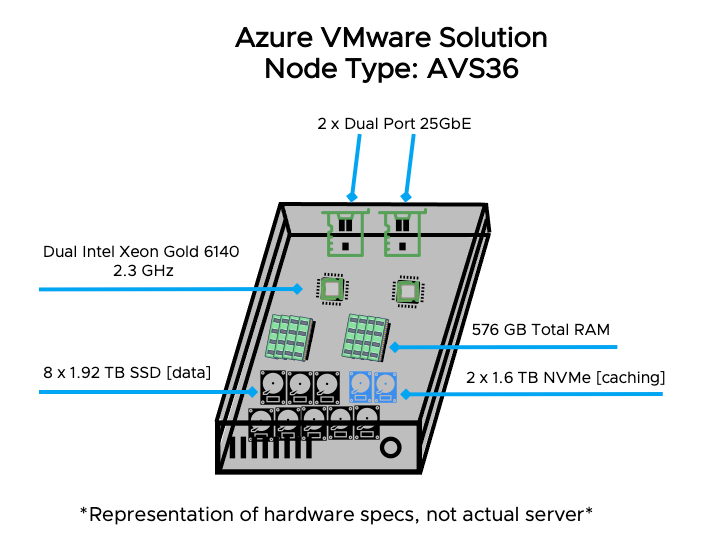
<p>A subscription can have 1-4 private clouds, each with a maximum of 4 clusters per cloud. An initial private cloud deployment starts with a 3-node minimum with the opportunity to add additional nodes during or scale-up later to a maximum of 16 nodes per cluster in the Azure portal. The hardware specification dropdown lists AVS36 as the current selectable node type. Below is a visual representation of the hardware specs for the AVS36, but it does not represent the actual server 🙂 An Azure Virtual Network (VNet) can be created during the initial private cloud deployment or afterward. If an existing VNet exists, it can also be used. A VNet is created to support an ExpressRoute from Azure VMware Solution to connect to other Azure services and allow connectivity back to an on-premises environment via Azure Global Reach. Once ready, click review and create. After you verify everything entered is correct, click the magical create button and wait for roughly 2+hrs for the process to complete. The process is mostly self-service from the Azure portal allowing you to get from zero to a private cloud which includes:</p>

<ul>
  <li><span data-preserver-spaces="true">Provisioning of hardware and backbone networking</span></li>
  <li><span data-preserver-spaces="true">Installation and configuration of ESXi, vCenter Server, vSAN, NSX-T, and HCX</span></li>
  <li><span data-preserver-spaces="true">Creation of initial cluster including vSAN datastore encryption</span></li>
</ul>

<blockquote class="prompt-info">
  <p>Note: if you don’t have an Azure ExpressRoute, you can use a site-to-site VPN to connect to Azure VMware Solution private cloud, but you will not be able to use HCX for workload migration as this is not supported.</p>
</blockquote>

<p><img src="https://emadyounis.com/assets/img/2020/09/AVS-Server.jpg?resize=703%2C560" alt="" /></p>

<h2 id="post-deployment">Post Deployment</h2>

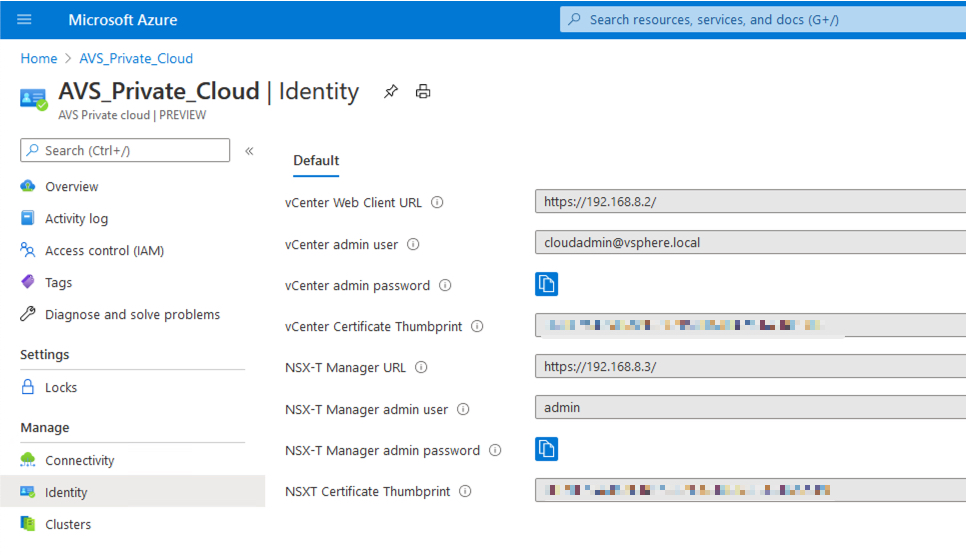
<p>When your private cloud is ready, you’ll be redirected to the overview page in the resource menu. This page is handy with valuable information; you can always come back here by searching your private cloud name or simply bookmarking. The first section we’ll want to select is identity. Here is where you’ll find your login information for NSX Manager and vCenter Server. Next is clustering, where you can edit (aka increase/decrease) the number of nodes in a private cloud, with 3 being the magic number of minimum nodes. Keep in mind increasing the number of nodes is tied to your allocation associated with the subscription used.</p>

<p><img src="https://emadyounis.com/assets/img/2020/09/Azure-VMware-Solution-Identity-Final-Image.jpg?resize=966%2C555" alt="" /></p>

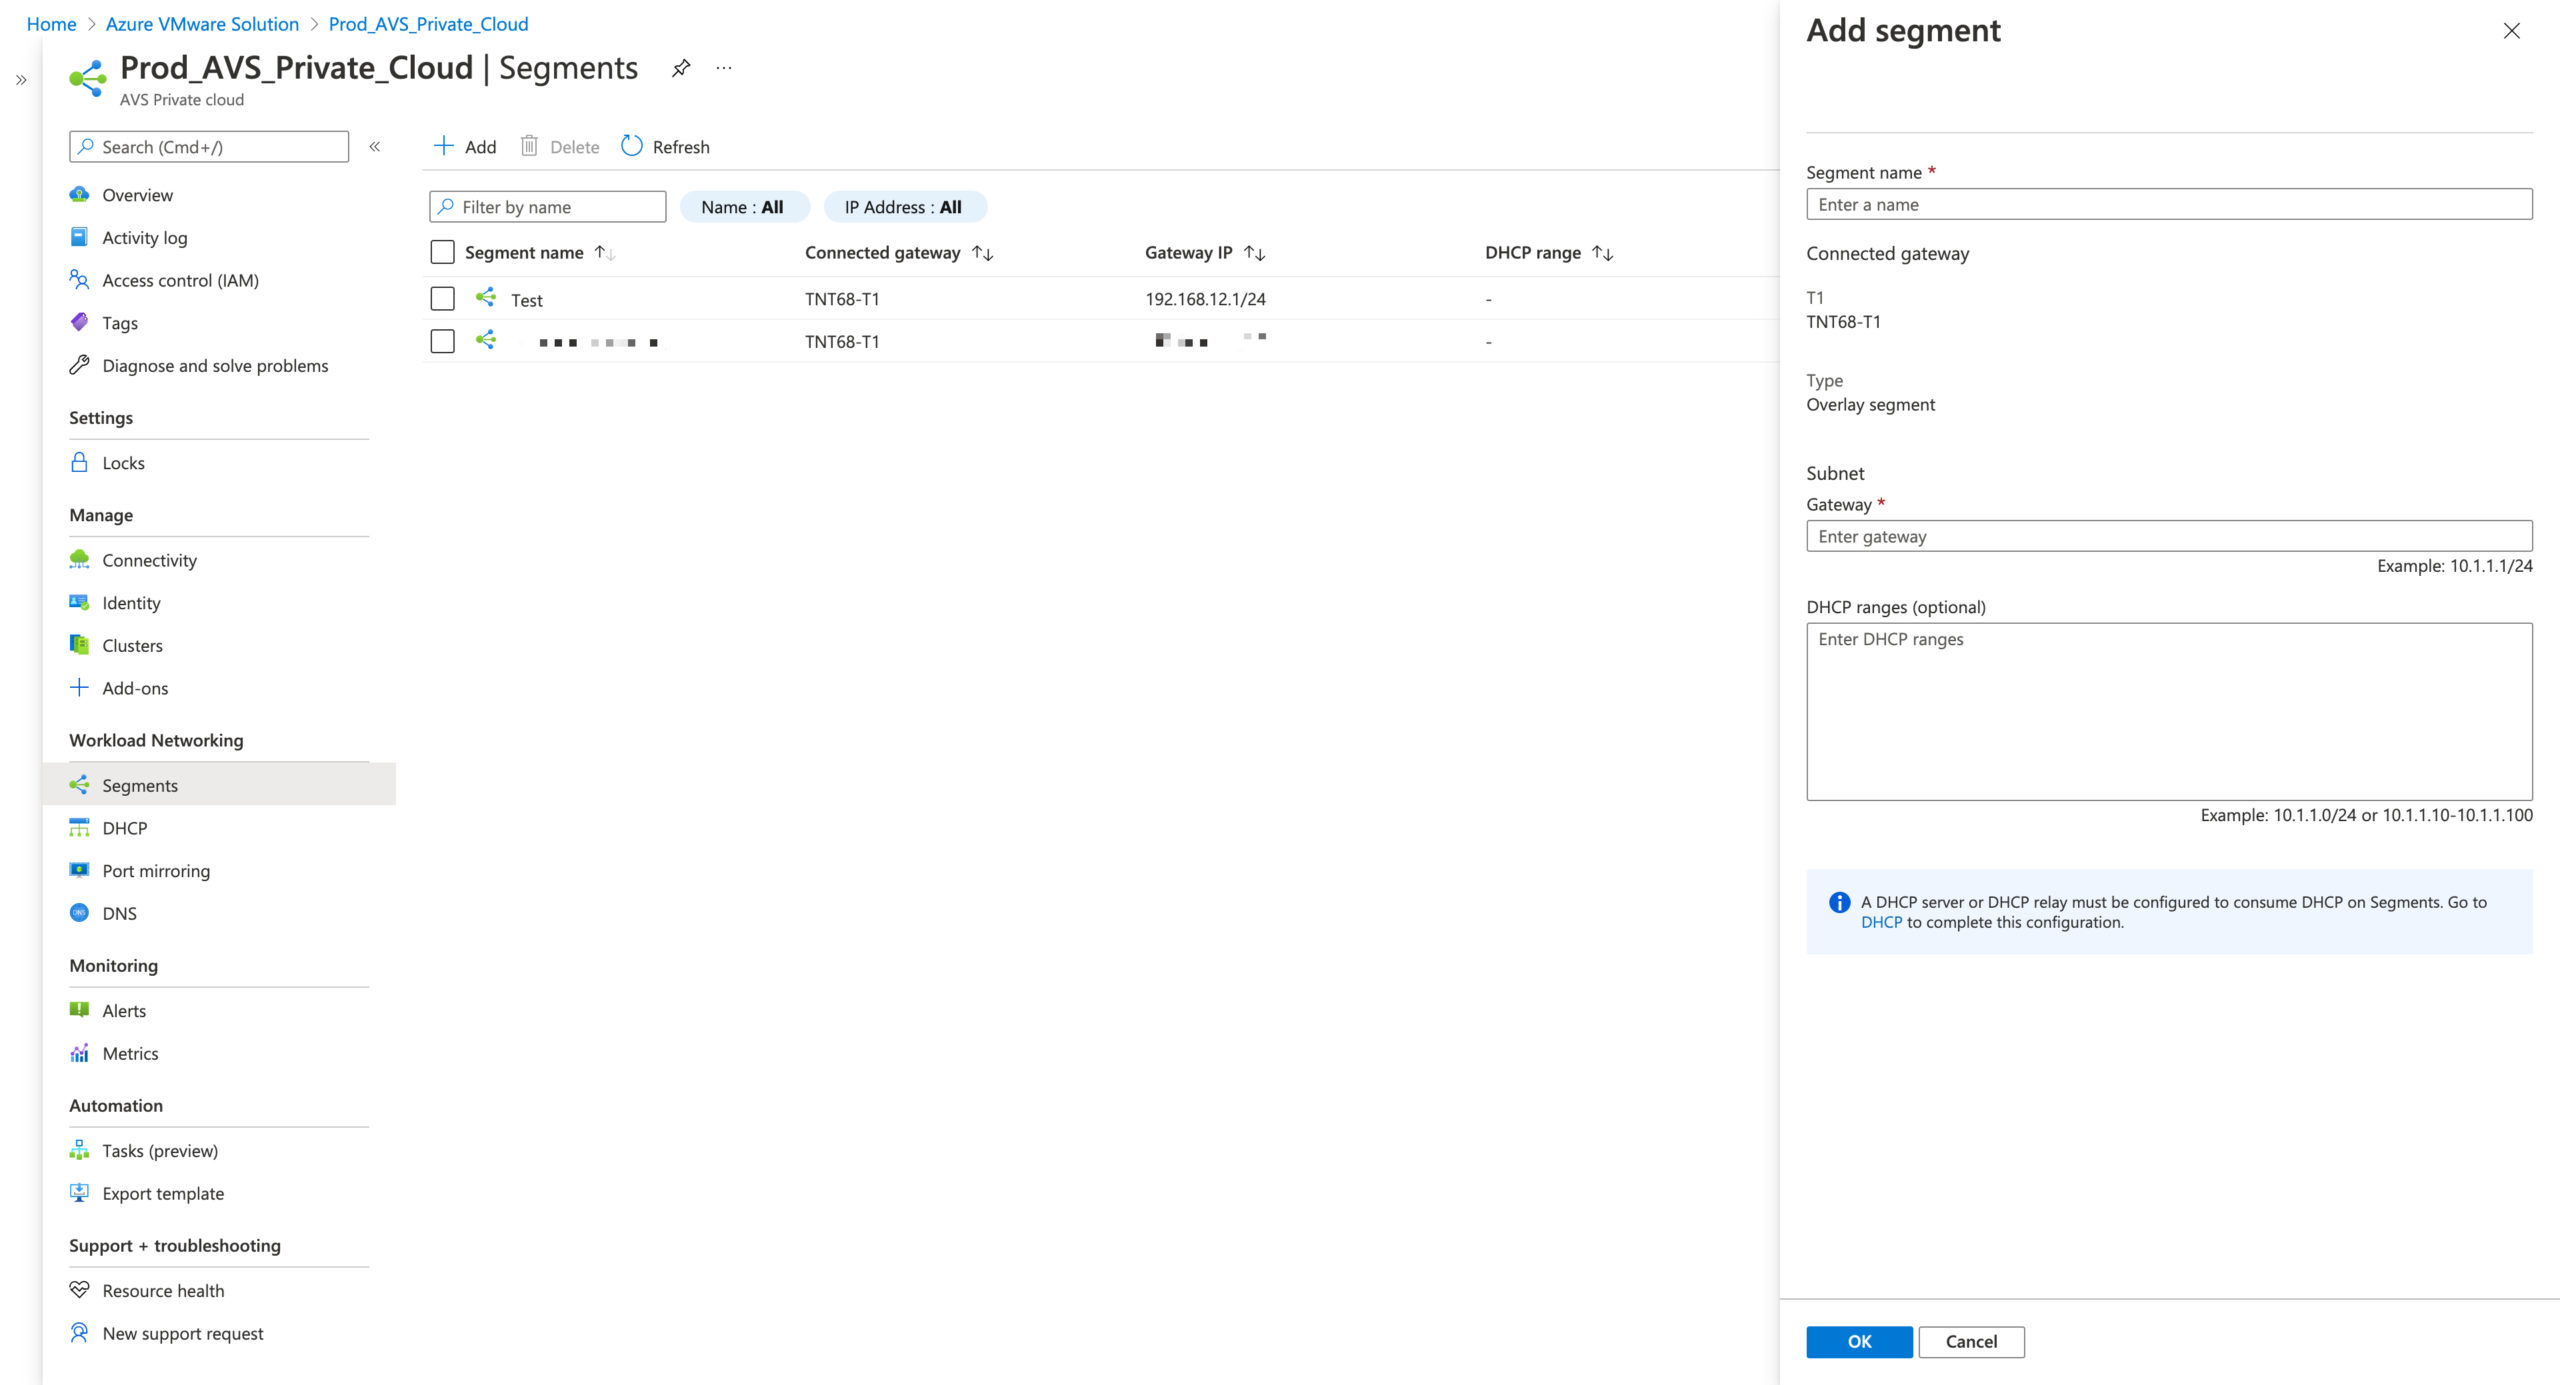
<p>The NSX T-1 router is where all workload network segments need to be created before VMs are deployed or being migrated to a new segment. These segments can be created in NSX manager or directly in the Azure Portal under segments, including the ability to create DHCP servers to handle DHCP requests and DHCP relay services to relay DHCP traffic to external DHCP servers. Additional workload networking options such as port mirroring and DNS are also available.</p>

<p><img src="https://emadyounis.com/assets/img/2020/09/AVS-Workload-Networking-scaled.jpg?resize=2560%2C1385" alt="" /></p>

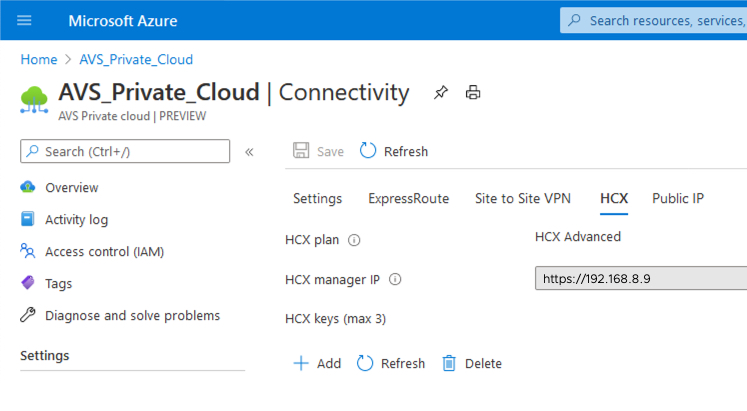
<p>I’ve mentioned VMware HCX; the good news, it’s automatically deployed as part of the private cloud provisioning. The HCX Cloud manager is where you’ll get the necessary HCX Connector bits to deploy in your on-premises environment, which can be found under the connectivity section in the Azure portal of your private cloud. The HCX Cloud manager address is provided, and you will use cloudadmin@vsphere.local credentials to login and download the HCX connector bits. Licensing your HCX connector is also part of the self-service offering, allowing you to request up to 3 advanced licenses. Additionally, there is an option to upgrade your HCX advanced license to an HCX enterprise license by opening a support request with Microsoft. HCX enterprise will provide features like mobility groups, replication assisted vMotion, mobility optimized networking, and more. These features make use cases like datacenter extension and evacuation easier to any VMware powered cloud.</p>

<p><img src="https://emadyounis.com/assets/img/2020/09/Azure-VMware-Solution-HCX-Final-Image.jpg?resize=747%2C411" alt="" /></p>

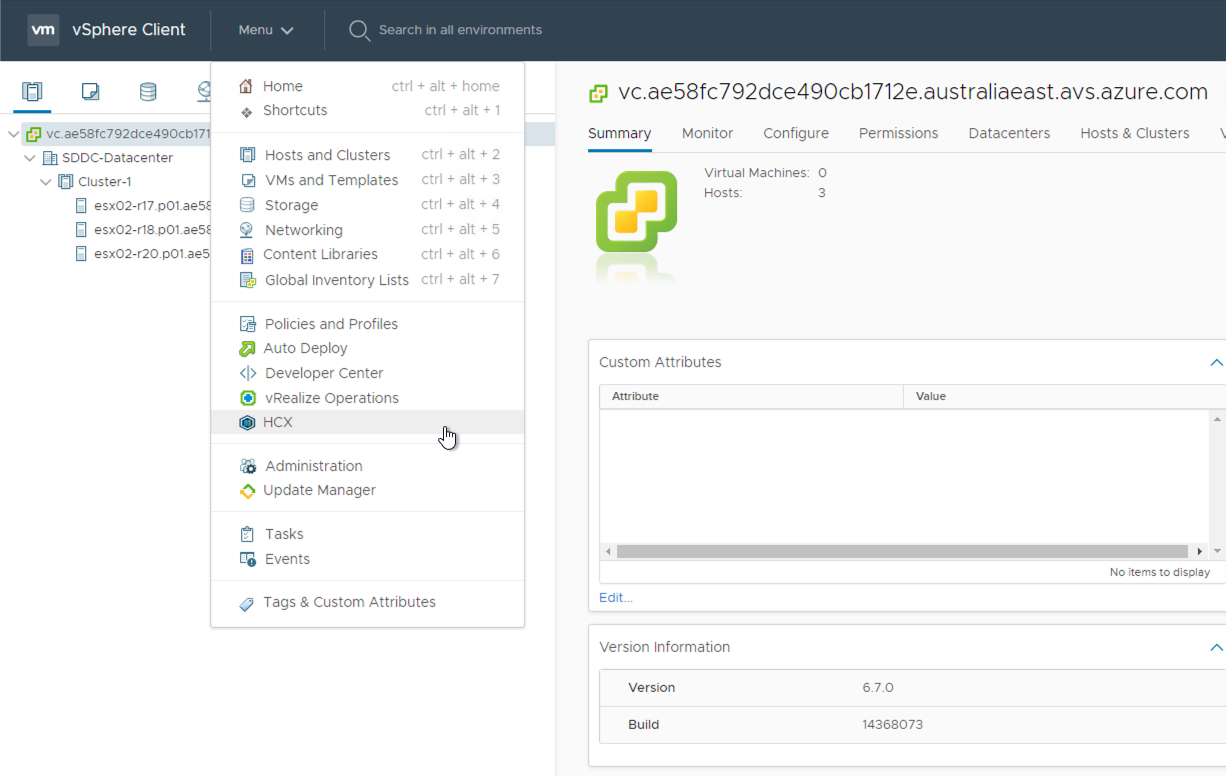
<p>Once the HCX connector is deployed and configured on-premises, customers can access and manage directly from the vSphere client, the dedicated HCX Client, or via automation using PowerCLI or REST APIs. A site pairing can then be established with on-premises environments and an Azure VMware Solution private cloud, followed by L2 connectivity for workloads that will retain their IP addresses. Let the migration planning begin!</p>

<p><img src="https://emadyounis.com/assets/img/2020/09/Azure-VMware-Solution-vCenter-Final-Image.jpg?resize=1226%2C776" alt="" /></p>

<p><span data-preserver-spaces="true">There are additional support and licensing benefits that come with Azure VMware Solution. </span><a href="https://support.microsoft.com/en-us/help/4456242/end-of-support-for-sql-server-2008-and-sql-server-2008-r2"><span data-preserver-spaces="true">Microsoft</span></a><span data-preserver-spaces="true"> is providing extended support for Windows Server 2008 and SQL SQL 2008 workloads when they are migrated to Azure, including the Azure VMware Solution. There is also the </span><a href="https://azure.microsoft.com/en-us/pricing/hybrid-benefit/"><span data-preserver-spaces="true">Azure Hybrid Benefit</span></a><span data-preserver-spaces="true"> which is a licensing benefit allowing customers to use their on-premises Windows Server and SQL Server licenses on Azure.</span></p>

<h2 id="resources">Resources</h2>

<p>Here are a few resources help get you started in learning more about Azure VMware Solution and more will be added as they are available. Also please reach out if you know of any others!</p>

<ul>
  <li><a href="http://hol.pub/avs">VMware Hands On Lab Azure VMware Solution</a></li>
  <li><a href="https://docs.microsoft.com/en-us/azure/azure-vmware/azure-vmware-solution-platform-updates?WT.mc_id=enterprise-0000-shkuehn">Platform updates for Azure VMware Solution</a></li>
  <li><a href="https://docs.microsoft.com/en-us/azure/azure-vmware/faq">FAQ: Common questions about Azure VMware Solution</a></li>
  <li><a href="https://www.vmworld.com/en/video-library/video-landing.html?sessionid=1586528544020001TS4T">VMworld: Azure VMware Solution Networking &amp; Security in a Hybrid Cloud Environment</a></li>
  <li><a href="https://azure.microsoft.com/en-us/services/azure-vmware/">Azure VMware Solution Product Page</a></li>
  <li><a href="https://docs.microsoft.com/en-us/azure/azure-vmware/">Azure VMware Solution Documentation</a></li>
  <li><a href="https://www.youtube.com/watch?v=qASXi5xrFzM&amp;list=PLS9k3ksxRe_l-UpfAjmi0BoDSpo6AtLyh">Video Playlist from Microsoft Global Blackbelt Trevor Davis</a></li>
  <li><a href="https://www.virtualworkloads.com/">Virtual Workloads Blog – Trevor Davis</a></li>
  <li><a href="https://myignite.microsoft.com/sessions/adcaabd7-9038-45d0-8e41-cf5fa3be5f1e">Microsoft Ignite 2020 Session: Accelerate your Cloud Journey with Azure VMware Solution</a></li>
  <li><a href="https://myignite.microsoft.com/sessions/1515e183-53a5-49e0-b39a-34c81d913ed2">Microsoft Ignite 2020 Session: An introduction to Azure VMware Solution</a></li>
  <li><a href="https://docs.microsoft.com/en-us/azure/azure-vmware/vrealize-operations-for-avs">Set up vRealize Operations for Azure VMware Solution</a></li>
  <li><a href="https://docs.vmware.com/en/VMware-Horizon/2006/horizon-installation/GUID-76CF25F7-B26A-4C6D-A5C5-F18D3A56590A.html">Deploying VMware Horizon on Azure VMware Solution</a></li>
</ul>]]></content><author><name>Emad Younis</name></author><category term="Azure VMware Solution" /><category term="Azure" /><category term="Cloud" /><category term="Microsoft" /><category term="VMware Cloud" /><summary type="html"><![CDATA[The general availability (GA) for the next evolution of Azure VMware Solution (AVS) was announced yesterday during the Microsoft Ignite 2020 virtual conference. This is a joint partnership between Microsoft and VMware, where Azure VMware Solution is a Microsoft managed service built on Azure bare metal infrastructure and cloud verified by VMware. The initial launch of the Azure VMware Solution in May of 2019 was by CloudSimple; this latest release is built and architected by Microsoft, providing an integrated experience with Azure services. Azure VMware Solution is currently available in the following 10 regions: East US, North Central US, West US, UK South, Japan East, West Europe, North Europe, Canada Central, Australia East, and Southeast Asia. More regions will be available in the future; additional details can be found by searching the Microsoft Products available by region page. Customers running the CloudSimple Azure VMware Solution version also have a migration path to this latest release, leveraging VMware HCX.]]></summary><media:thumbnail xmlns:media="http://search.yahoo.com/mrss/" url="https://emadyounis.com/assets/img/Feature-Images/Azure-VMware-Solution-Feature-Image.png" /><media:content medium="image" url="https://emadyounis.com/assets/img/Feature-Images/Azure-VMware-Solution-Feature-Image.png" xmlns:media="http://search.yahoo.com/mrss/" /></entry><entry><title type="html">Introduction to Google Cloud VMware Engine</title><link href="https://emadyounis.com/introduction-to-google-cloud-vmware-engine/" rel="alternate" type="text/html" title="Introduction to Google Cloud VMware Engine" /><published>2020-07-06T11:22:26-07:00</published><updated>2020-07-06T11:22:26-07:00</updated><id>https://emadyounis.com/introduction-to-google-cloud-vmware-engine</id><content type="html" xml:base="https://emadyounis.com/introduction-to-google-cloud-vmware-engine/"><![CDATA[<p>Last month <a href="https://cloud.google.com/blog/topics/hybrid-cloud/announcing-google-cloud-vmware-engine">Google announced</a> a first-party and fully managed solution called Google Cloud VMware Engine (GCVE), which was in limited early access since January 2020. Google Cloud VMware Engine is <a href="https://cloud.google.com/blog/topics/hybrid-cloud/google-cloud-vmware-engine-is-generally-available">now generally available</a> to all starting in US-east and US-west regions with plans to add eight more regions by the end of the year. When deployed, customers will receive a GCVE private cloud, which consists of ESXi Hosts, vCenter Server, vSAN, and NSX-T running on Google Cloud bare metal. Also included is VMware HCX, which allows customers to extend and migrate workloads from on-premises to GCVE and between GCVE private clouds.</p>
<p>As part of the GCVE service availability, customers have several pricing options: on-demand (per-hour), 1yr commitment, and 3yr commitment, which includes the cost of infrastructure, licensing, and support. Billing is handled through Google Cloud; for more details, please see the <a href="https://cloud.google.com/vmware-engine#section-13">following</a>. The GCVE service allows customers to focus on workloads while Google manages all other aspects of the service, including the lifecycle of the vSphere environment.</p>

<p><img src="https://emadyounis.com/assets/img/2020/07/GCVE-Welcome.jpg?resize=1024%2C457" alt="" /></p>

<h2 id="gcve-service"><span style="color: #000000;">GCVE Service</span></h2>

<p><span style="color: #000000;"><span style="color: #000000;"><strong>* Project – must be created as part of the Google Cloud service and is a way to group and manage resources.</strong><br />
 <strong>* Private Cloud – is the equivalent of a VMware Software-Defined Data Center (vCenter Server, ESXi, vSAN, and NSX).</strong> </span></span></p>

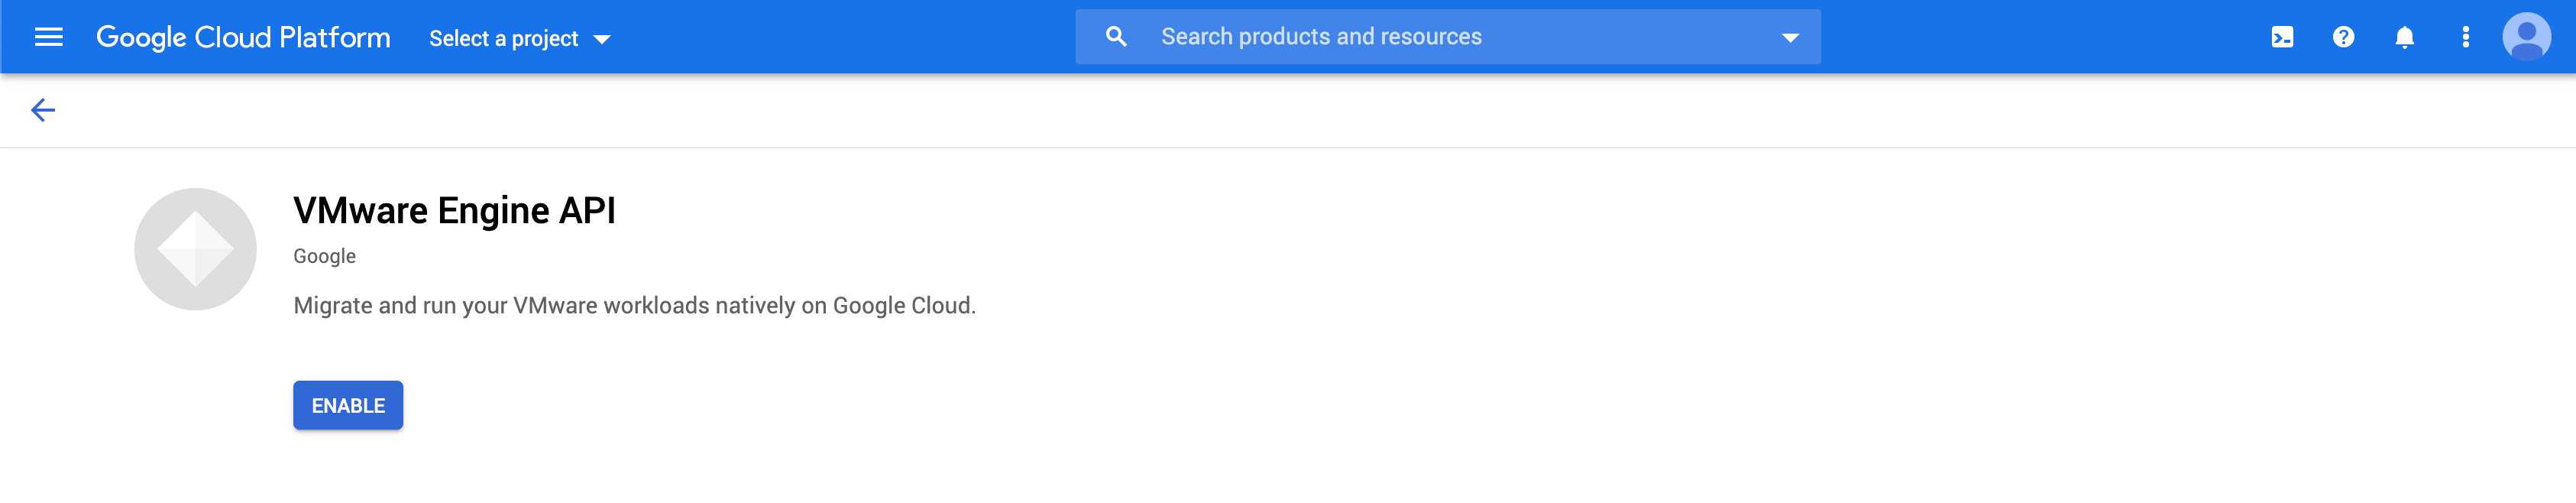
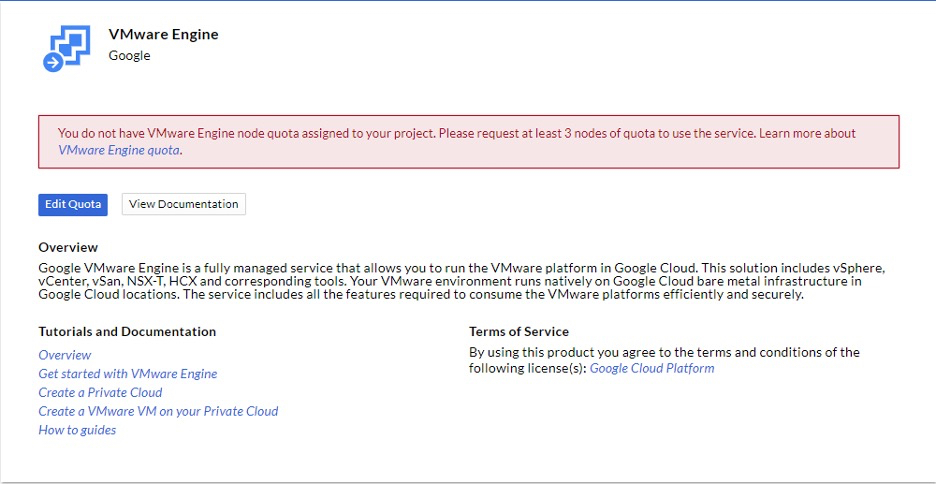
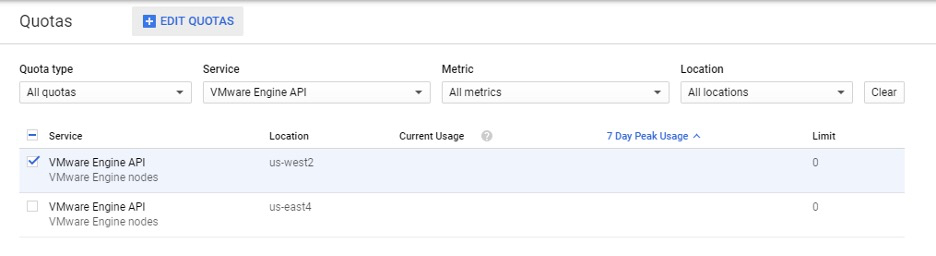
<p>To get started with GCVE first requires enabling the VMware Engine API in the Google Cloud console. This will need to be done on a per-project basis. Next, you’ll need to request a quota which is located under IAM &amp; Admin. A quota is a way to verify, protect against unexpected usage, and prevent misuse. Each project in Google Cloud could have a different quota. Once your quota request has been accepted, we can start <a href="https://cloud.google.com/vmware-engine/docs/quickstart-prerequisites">getting ready</a> to deploy a GCVE private cloud.</p>

<p><img src="https://emadyounis.com/assets/img/2020/07/GCVE-Enable-API.jpg?resize=1024%2C200" alt="" /></p>

<p>The GCVE service configuration will consist of a minimum of 3 nodes and can scale up to 16 nodes per cluster (roughly 15 mins per node add) or 64 nodes in a single private cloud. Each GCVE node has the following specifications:</p>

<ul>
  <li>
    <ul>
      <li><strong>CPU</strong> – 2x Intel Xeon Gold 6240 (Cascade Lake) 2.6 GHz, 36 Cores, 72 Hyper-Threads
        <ul>
          <li><strong>Memory</strong> – 768 GB</li>
          <li><strong>Storage:</strong>
            <ul>
              <li>2x 1.6 TB (3.2 total TB) NVMe for cache</li>
              <li>6 x 3.2 TB (19.2 TB Total) NVMe for data</li>
            </ul>
          </li>
          <li><strong>Network</strong> – 4 x Dual Port 25GbE</li>
        </ul>
      </li>
    </ul>
  </li>
</ul>

<p>GA included <a href="https://cloud.google.com/vmware-engine/docs/concepts-vmware-components">software specifications</a> (keep in mind these versions will change over time):</p>

<p>[table id=14 /]</p>

<p><img src="https://emadyounis.com/assets/img/2020/07/GCVE-Quota-1.jpg?resize=936%2C484" alt="" /></p>

<p><img src="https://emadyounis.com/assets/img/2020/07/GCVE-Quota-2.jpg?resize=936%2C256" alt="" /><br />
Part of the <a href="https://cloud.google.com/vmware-engine/sla"><span data-preserver-spaces="true">service level agreement</span></a><span data-preserver-spaces="true"> (SLA) ensures customers have the needed reliability. GCVE is providing 99.99% of network uptime (less than an hour per year) for its service and has network redundancy across rack configuration. Connectivity from on-premises to GCVE (or between private clouds within GCVE) can be established using a </span><a href="https://cloud.google.com/network-connectivity/docs/vpn"><span data-preserver-spaces="true">Google Cloud VPN</span></a><span data-preserver-spaces="true">, the quickest method (self-service) to getting started. There is also the option to use Google’s</span><a href="https://cloud.google.com/network-connectivity/docs/how-to/how-to-choose#cloud-interconnect"><span data-preserver-spaces="true"> Cloud Interconnect</span></a><span data-preserver-spaces="true"> (available from Google or </span><a href="https://cloud.google.com/network-connectivity/docs/interconnect/concepts/service-providers"><span data-preserver-spaces="true">Service Providers</span></a><span data-preserver-spaces="true">), a dedicated, highly available, low latency direct connection. As part of the configuration process, customers will need to create Virtual Private Cloud (VPC) within the Google Cloud that allows them to control how workloads connect within a region or globally, create policies within projects, and expand IP spaces without downtime. After the VPC is created, workloads can communicate internally within a project, keeping traffic local and providing extensibility to Google Cloud Services.</span></p>

<p>A CIDR block is required to deploy all the vSphere management components within GCVE, but workload networks will be provisioned from NSX-T (NSX segments). There will be DNS servers deployed within a private cloud and are only used for management. Within the network section of the GCVE console, customers can allocate public IP addresses to workloads, which are protected by Google Cloud Edge. The VPN Gateway section provides a point to site VPN that gives access to the management components like vCenter Server within GCVE.</p>

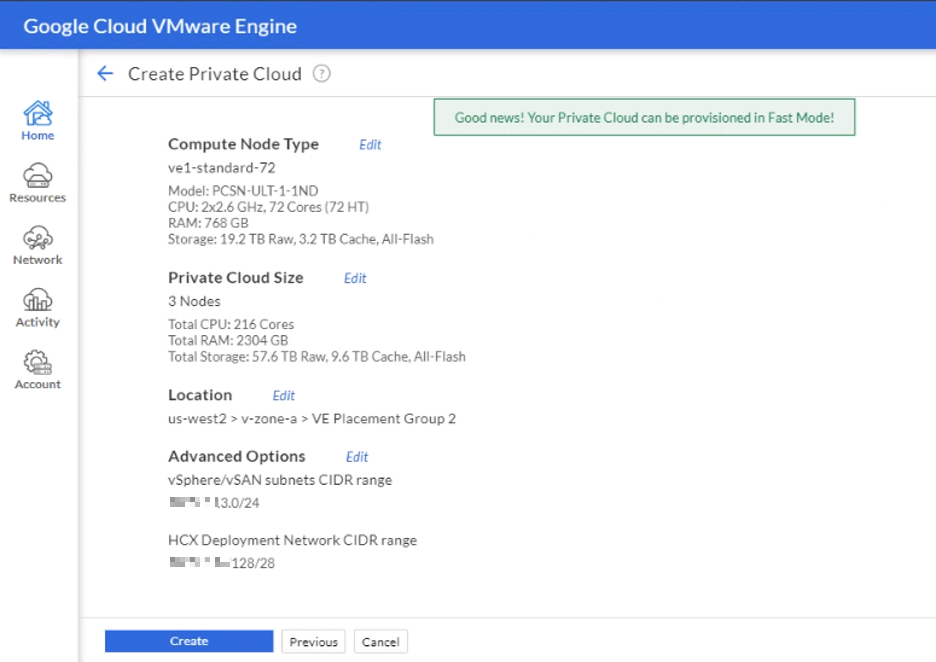
<p><span data-preserver-spaces="true">There are a couple of things I want to highlight within the GCVE service. First, when it comes to deploying a private cloud, GCVE has fast provisioning, where it takes approximately 30 minutes to deploy a private cloud with all components running (the clock starts when you click on create). On the back end, the GCVE service has built-in intelligence and optimization magic sauce allowing it to pre-provision capacity on unused nodes before they are requested. These nodes are then re-purposed based on the customer’s specifications and capacity. This ensures deployments are the same as if they were installed from scratch.</span></p>

<p><img src="https://emadyounis.com/assets/img/2020/07/GCVE-Fast-Mode.jpg?resize=936%2C662" alt="" /></p>

<p><span data-preserver-spaces="true">Second, is how Role-Based Access Control (RBAC) works in GCVE. It starts with the Google Cloud console, to gain access to GCVE you either have to be an owner or editor of a project in the Google Cloud console or granted the following roles within a project’s IAM roles and permissions:</span></p>

<ul>
  <li>
    <ul>
      <li>
        <ul>
          <li><span data-preserver-spaces="true">VMware Engine Service Viewer (read-only access)</span>
            <ul>
              <li><span data-preserver-spaces="true">VMware Engine Service admin (full admin access)</span></li>
            </ul>
          </li>
        </ul>
      </li>
    </ul>
  </li>
</ul>

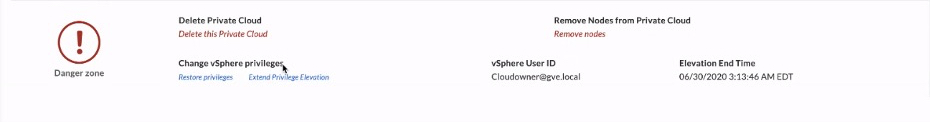
<p>Once access has been granted, the GCVE portal has three RBAC options: CloudOwner, Elevated Privilege, and Service Provider. The CloudOwner account is the default account; it allows customers the access needed to handle their day-to-day operations on their workloads and provides full access to NSX-T networking (including NSX-T manager). Elevated privilege is a temporary and time-based request that allows access to hosts, storage, and management VMs to create and add identity sources and auth management; this level of access is monitored. The GCVE service monitors actions of the elevate privilege and provides notification if an action is disruptive to the service and the customer, potentially preventing those actions from happening. It also allows the creation and addition of accounts necessary for 3rd party integration, such as backup solutions. Customers can request Elevated Privilege within the GVCE portal on-demand. Service Provider access is only available for Google support only and provides full access to the customer’s private cloud within GCVE for troubleshooting.</p>

<p>When first logging into vSphere Client, you will be prompted to <a href="https://cloud.google.com/vmware-engine/docs/vmware-platform/howto-access-vsphere-client">change</a> the default CloudOwner@gve.local account password, which must be changed every 365 days afterward. There are also some pre-created roles that can be used, or you can create your own, but no role can be granted privileges higher than CloudOwner. You can find a list of the GCVE vCenter Server roles and privileges <a href="https://cloud.google.com/vmware-engine/docs/concepts-permission-model">here</a>. GCVE also supports adding your identity solution, which allows you to use your on-premises groups in vCenter Server.</p>

<p><img src="https://emadyounis.com/assets/img/2020/07/GCVE-Elevated-Privileges-Updated.jpg?resize=930%2C122" alt="" /></p>

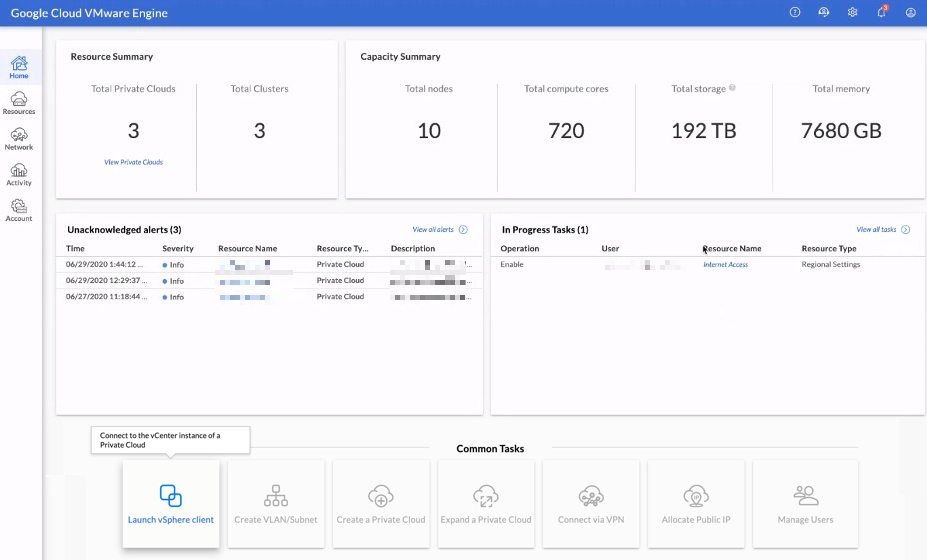
<p>All service and access configurations are done from the GCVE console; this includes launching the vSphere Client, network configuration/management, and Private Cloud management (deployment, configuration, and capacity). The GCVE console allows the management of different private clouds from a centralized location. It also provides an activity view that displays alarms, events, tasks, and audits, which tracks all the changes made across private clouds. Customers also have the option to download report information from various sections of the GCVE console in CSV format.</p>

<p><img src="https://emadyounis.com/assets/img/2020/07/GCVE-Console.jpg?resize=927%2C560" alt="" /></p>

<h2 id="workload-mobility">Workload Mobility</h2>

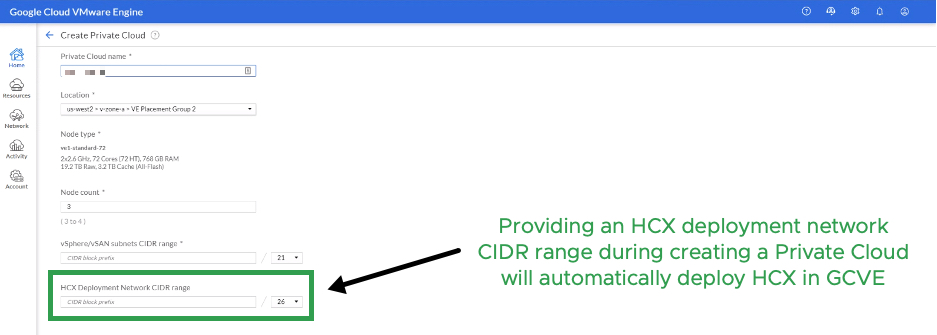
<p>Included with the GCVE service is <a href="https://cloud.google.com/vmware-engine/docs/workloads/howto-migrate-vms-using-hcx">VMware HCX</a> (advanced licensing), which allows customers to migrate workloads as far back as vSphere 5.0 from on-premises to GCVE without re-platforming. It’s the swiss army knife of workload mobility. VMware HCX Cloud Manager is deployed, configured, and licensed out of the box as part of the GCVE private cloud deployment, requiring a CIDR block for the VMware HCX components. Once the HCX Cloud Manager is deployed, customers can download the HCX Connector OVA to deploy in their on-premises data center, allowing them to pair with their GCVE private cloud. With a site pairing established, HCX provides the option to extend workload networks (L2 Stretch) and migrate using different migration types based on your SLAs: Bulk Migration – min downtime, vMotion – no downtime, and Cold Migration – downtime.</p>

<p>Additional functionality and migration types are also included with the HCX enterprise add-on licensing:</p>

<ul>
  <li>
    <ul>
      <li>
        <ul>
          <li>Replication Assisted vMotion – the ability to migrate with zero downtime
            <ul>
              <li>Mobility Groups -create migration groups based on criteria and migrate in waves</li>
              <li><a href="https://docs.vmware.com/en/VMware-HCX/services/user-guide/GUID-32AF32BD-DE0B-4441-95B3-DF6A27733EED.html">more</a></li>
            </ul>
          </li>
        </ul>
      </li>
    </ul>
  </li>
</ul>

<p>These are a few examples of what’s included with VMware HCX enterprise licensing, contact your VMware/Google representative for more details. This also simplifies uses cases such as data center evacuation, disaster recovery, and hybrid connectivity.</p>

<p><img src="https://emadyounis.com/assets/img/2020/07/GCVE-HCX-Deployment.jpg?resize=937%2C335" alt="" /></p>

<h2 id="resources">Resources</h2>

<p>With the launch of the new Google Cloud VMware Engine service I wanted to share some resources to help get you started and bookmark:</p>

<ul>
  <li>
    <ul>
      <li><a href="https://cloud.google.com/vmware-engine/docs">Google Cloud VMware Engine Documentation</a>
        <ul>
          <li><a href="https://cloud.google.com/vmware-engine/docs/release-notes">Release Notes</a></li>
          <li><a href="https://cloud.google.com/vmware-engine/docs/known-issues">Known Issues</a></li>
          <li><a href="https://cloud.google.com/vmware-engine/sla">Service Level Agreement</a></li>
          <li><a href="https://cloud.google.com/vmware-engine/docs/quickstart-prerequisites">Prerequisites</a></li>
          <li><a href="https://cloud.google.com/vmware-engine#section-13">Pricing</a></li>
          <li><a href="https://cloud.google.com/vmware-engine#section-14">Ecosystem Partners</a></li>
          <li><a href="https://cloud.withgoogle.com/next/sf/sessions#infrastructure">Google Cloud Next ’20</a> – Filtered with VMware as a Service</li>
        </ul>
      </li>
    </ul>
  </li>
</ul>]]></content><author><name>Emad Younis</name></author><category term="Google Cloud VMware Engine" /><category term="GCVE" /><category term="Google Cloud" /><category term="VMware" /><category term="VMware HCX" /><summary type="html"><![CDATA[Last month Google announced a first-party and fully managed solution called Google Cloud VMware Engine (GCVE), which was in limited early access since January 2020. Google Cloud VMware Engine is now generally available to all starting in US-east and US-west regions with plans to add eight more regions by the end of the year. When deployed, customers will receive a GCVE private cloud, which consists of ESXi Hosts, vCenter Server, vSAN, and NSX-T running on Google Cloud bare metal. Also included is VMware HCX, which allows customers to extend and migrate workloads from on-premises to GCVE and between GCVE private clouds.]]></summary><media:thumbnail xmlns:media="http://search.yahoo.com/mrss/" url="https://emadyounis.com/assets/img/Feature-Images/Introduction-to-Google-Cloud-VMware-Engine.png" /><media:content medium="image" url="https://emadyounis.com/assets/img/Feature-Images/Introduction-to-Google-Cloud-VMware-Engine.png" xmlns:media="http://search.yahoo.com/mrss/" /></entry><entry><title type="html">Uniquely Identifying Virtual Machines In VMware HCX</title><link href="https://emadyounis.com/uniquely-identifying-virtual-machines-in-vmware-hcx/" rel="alternate" type="text/html" title="Uniquely Identifying Virtual Machines In VMware HCX" /><published>2020-03-17T08:12:40-07:00</published><updated>2020-03-17T08:12:40-07:00</updated><id>https://emadyounis.com/uniquely-identifying-virtual-machines-in-vmware-hcx</id><content type="html" xml:base="https://emadyounis.com/uniquely-identifying-virtual-machines-in-vmware-hcx/"><![CDATA[<p>I’ve received several questions lately on what happens to a VM’s Managed Object Reference (MoRef) ID and InstanceUUID when it’s migrated across different vCenter Servers using VMware HCX. This information is essential for anything being used to identify VMs, such as provisioning systems, CMDBs, ticketing systems, and backup solutions are examples of tooling using this information.</p>
<p>When a VM gets created within a vCenter Server, it generates a MoRef ID that helps uniquely identify it. A MoRef ID gets created not just for VMs but all objects (hosts, folders, datastores, etc.) within a vCenter Server, including the vCenter Server itself. If you’ve heard me talk about using the vCenter Server Migration Tool (Windows to VCSA), I reference the importance of a vCenter Server keeping its MoRef ID, which is how other solutions will identify a vCenter Server. In this case, the Windows vCenter Server MoRef ID gets retained during the migration process, which means any registered solutions will continue to identify the original vCenter Server unknowingly of the migration process 🙂</p>

<p>Another way to uniquely identify a VM within a vCenter Server is by using its instanceUUID, introduced in vSphere 4.0. If you’ve explored inside the VM .vmx file, there is an entry called vc.uuid, which is a 128bit integer and looks something like “50 3e 84 9c 71 56 12 29-a6 a7 00 d3 3c a5 d3 28”. Both MoRef and InstanceUUID information is obtainable using the vSphere API. For more details, I recommend looking at the following blog posts by William Lam. This post builds on the information he provided, focusing on HCX migration types with VM MoRef ID and InstanceUUID.</p>

<ul>
  <li><a href="https://blogs.vmware.com/vsphere/2012/02/uniquely-identifying-virtual-machines-in-vsphere-and-vcloud-part-1-overview.html">Uniquely Identifying Virtual Machines in vSphere and vCloud Part 1: Overview</a></li>
  <li><a href="https://blogs.vmware.com/vsphere/2012/02/uniquely-identifying-virtual-machines-in-vsphere-and-vcloud-part-2-technical.html">Uniquely Identifying Virtual Machines in vSphere and vCloud Part 2: Technical</a></li>
  <li><a href="https://www.virtuallyghetto.com/2017/07/uniquely-identifying-vms-in-vsphere-part-3-enhanced-linked-mode-cross-vc-vmotion.html">Uniquely Identifying VMs in vSphere Part 3: Enhanced Linked Mode &amp; Cross VC-vMotion</a></li>
</ul>

<h2 id="hcx-vm-migrations">HCX VM Migrations</h2>

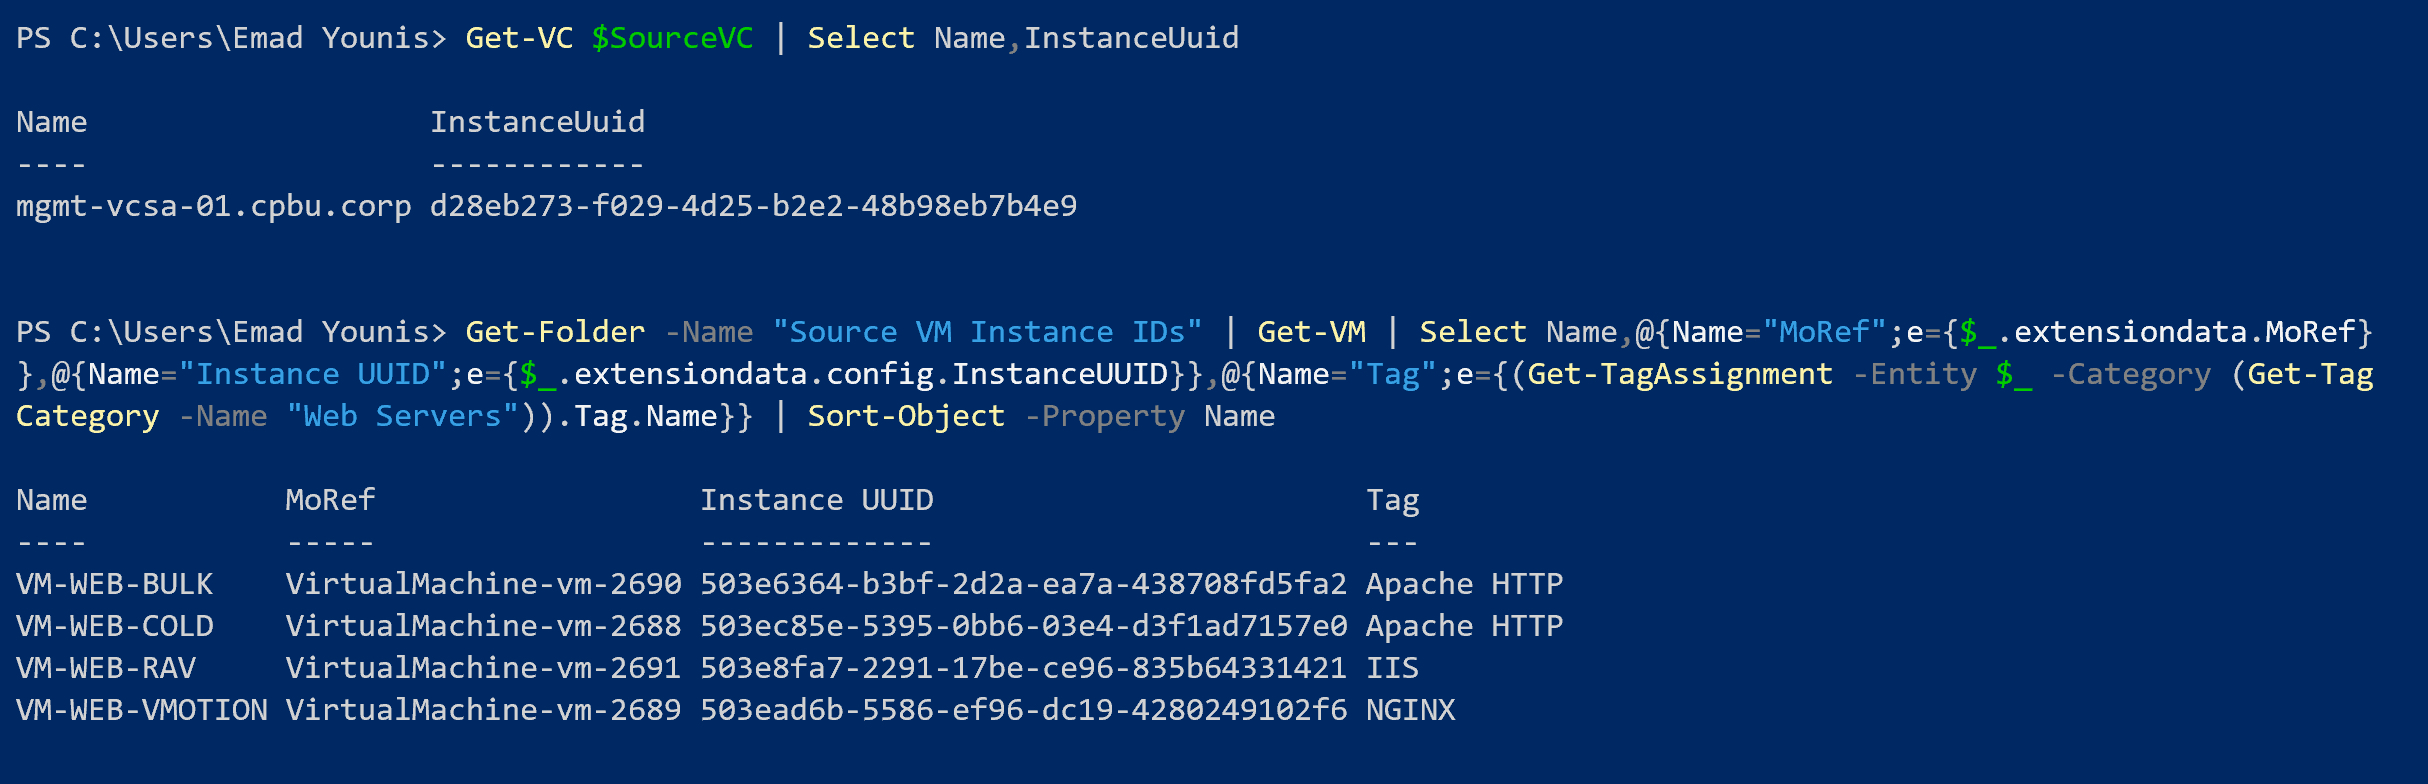
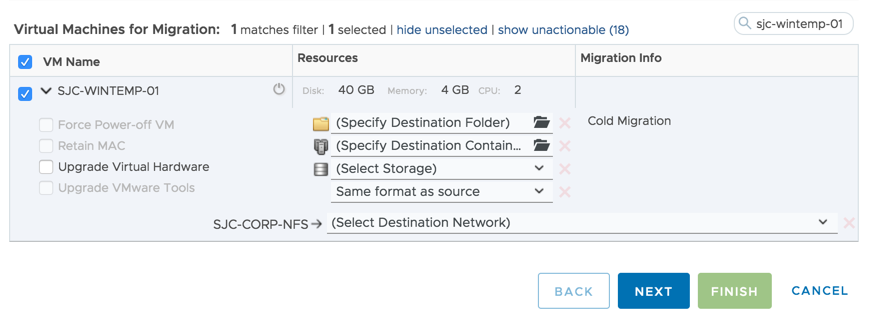
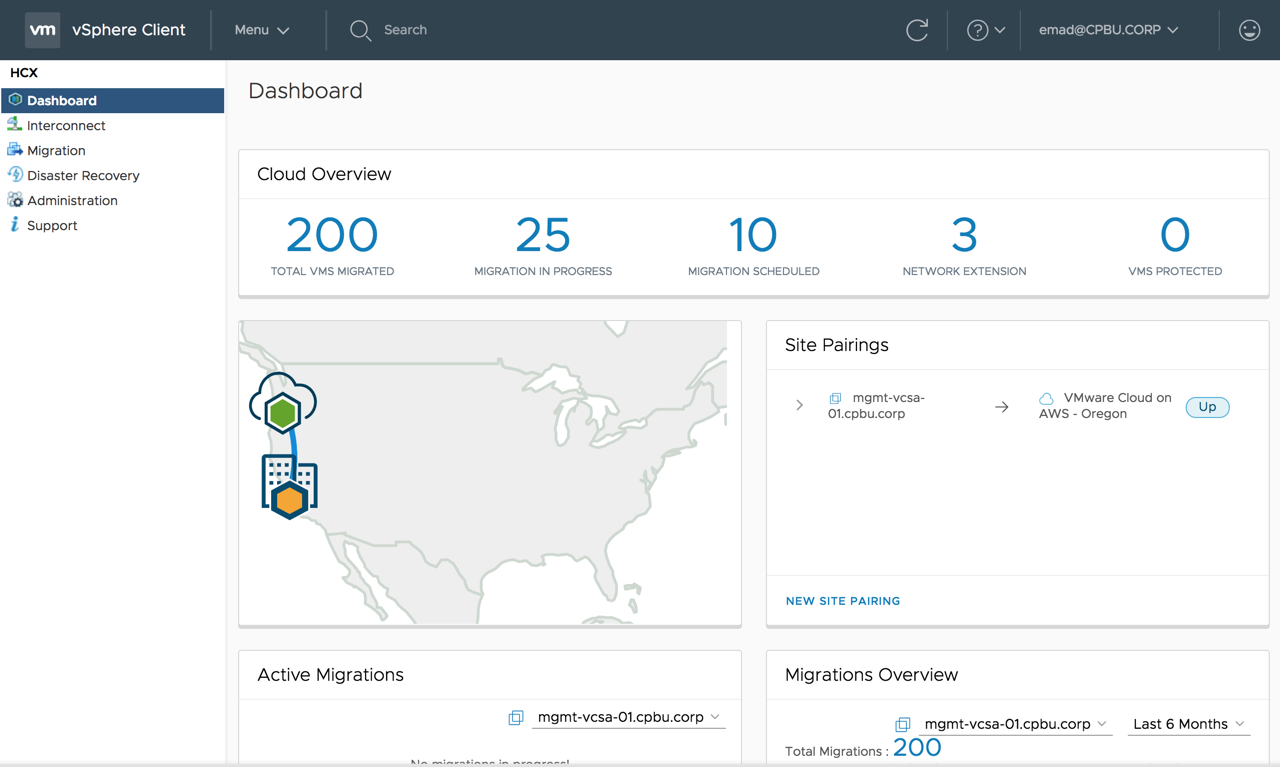
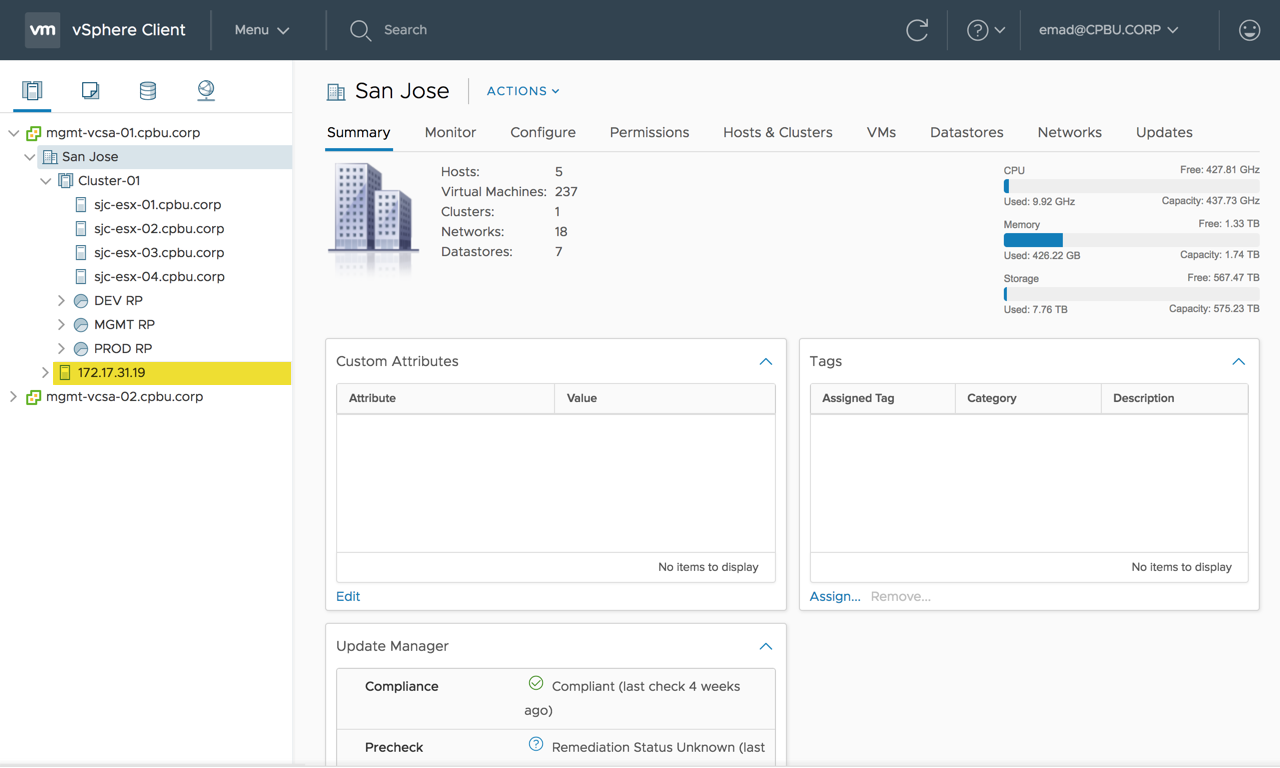
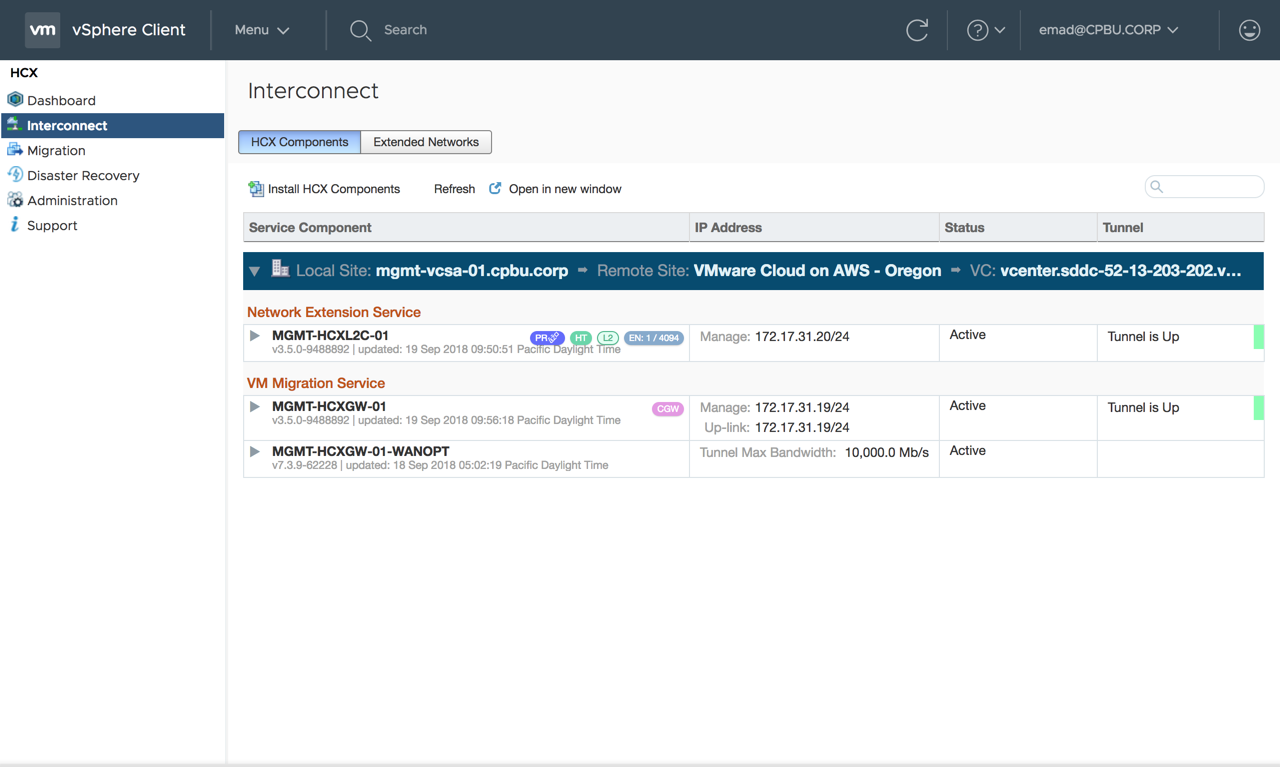
<p>With HCX, VMs can easily migrate using various <a href="http://emadyounis.com/learning-hybrid-cloud-extension-hcx-part-2-migration-types/">migration types</a> (Cold, vMotion, Bulk, RAV) between vCenter Servers, whether on-prem vSphere (5.0-7.0) or cloud (VMware Cloud on AWS, Azure VMware Solutions, etc.). In this example, I have a source on-prem vCenter Server using HCX to migrate VMs to the destination vCenter Server in VMware Cloud on AWS (VMC). Each VM name contains the migration type that will be used when its migrated to VMC with HCX. Before starting the migration, I grabbed the MoRef ID, InstanceUUID, and Tag for each VM as well as the source vCenter Server Name and its InstanceUUID.</p>

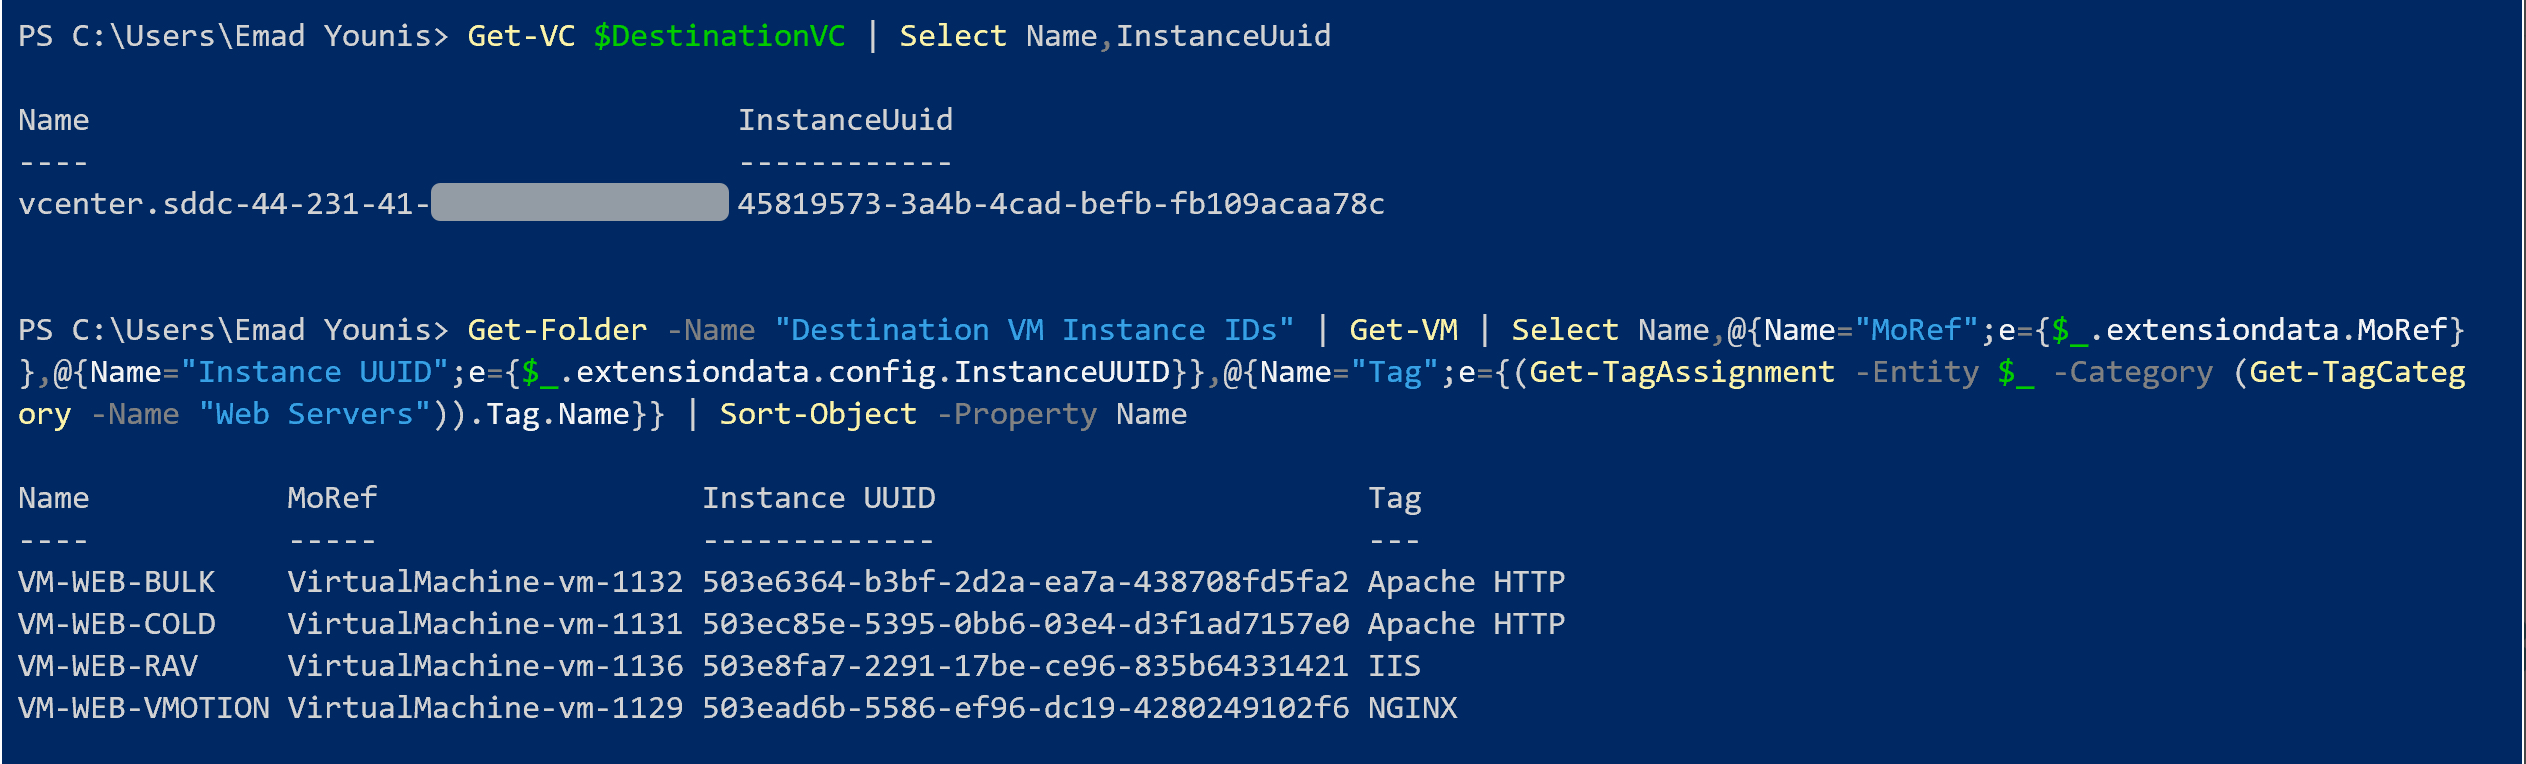
<p><img src="https://emadyounis.com/assets/img/2020/03/Source.jpg?resize=1024%2C331" alt="" /><br />
After the migrations completed successfully to the destination vCenter Server, we can see only one difference. All the VMs received a new MoRef ID, which is as expected since its managed per vCenter Server independently. The VM instanceUUID did not change, and <span style="color: #000000;">will only change if a VM with the same UUID already exists </span>on the destination vCenter Server.</p>

<p><img src="https://emadyounis.com/assets/img/2020/03/Destination.jpg?resize=1024%2C310" alt="" /><br />
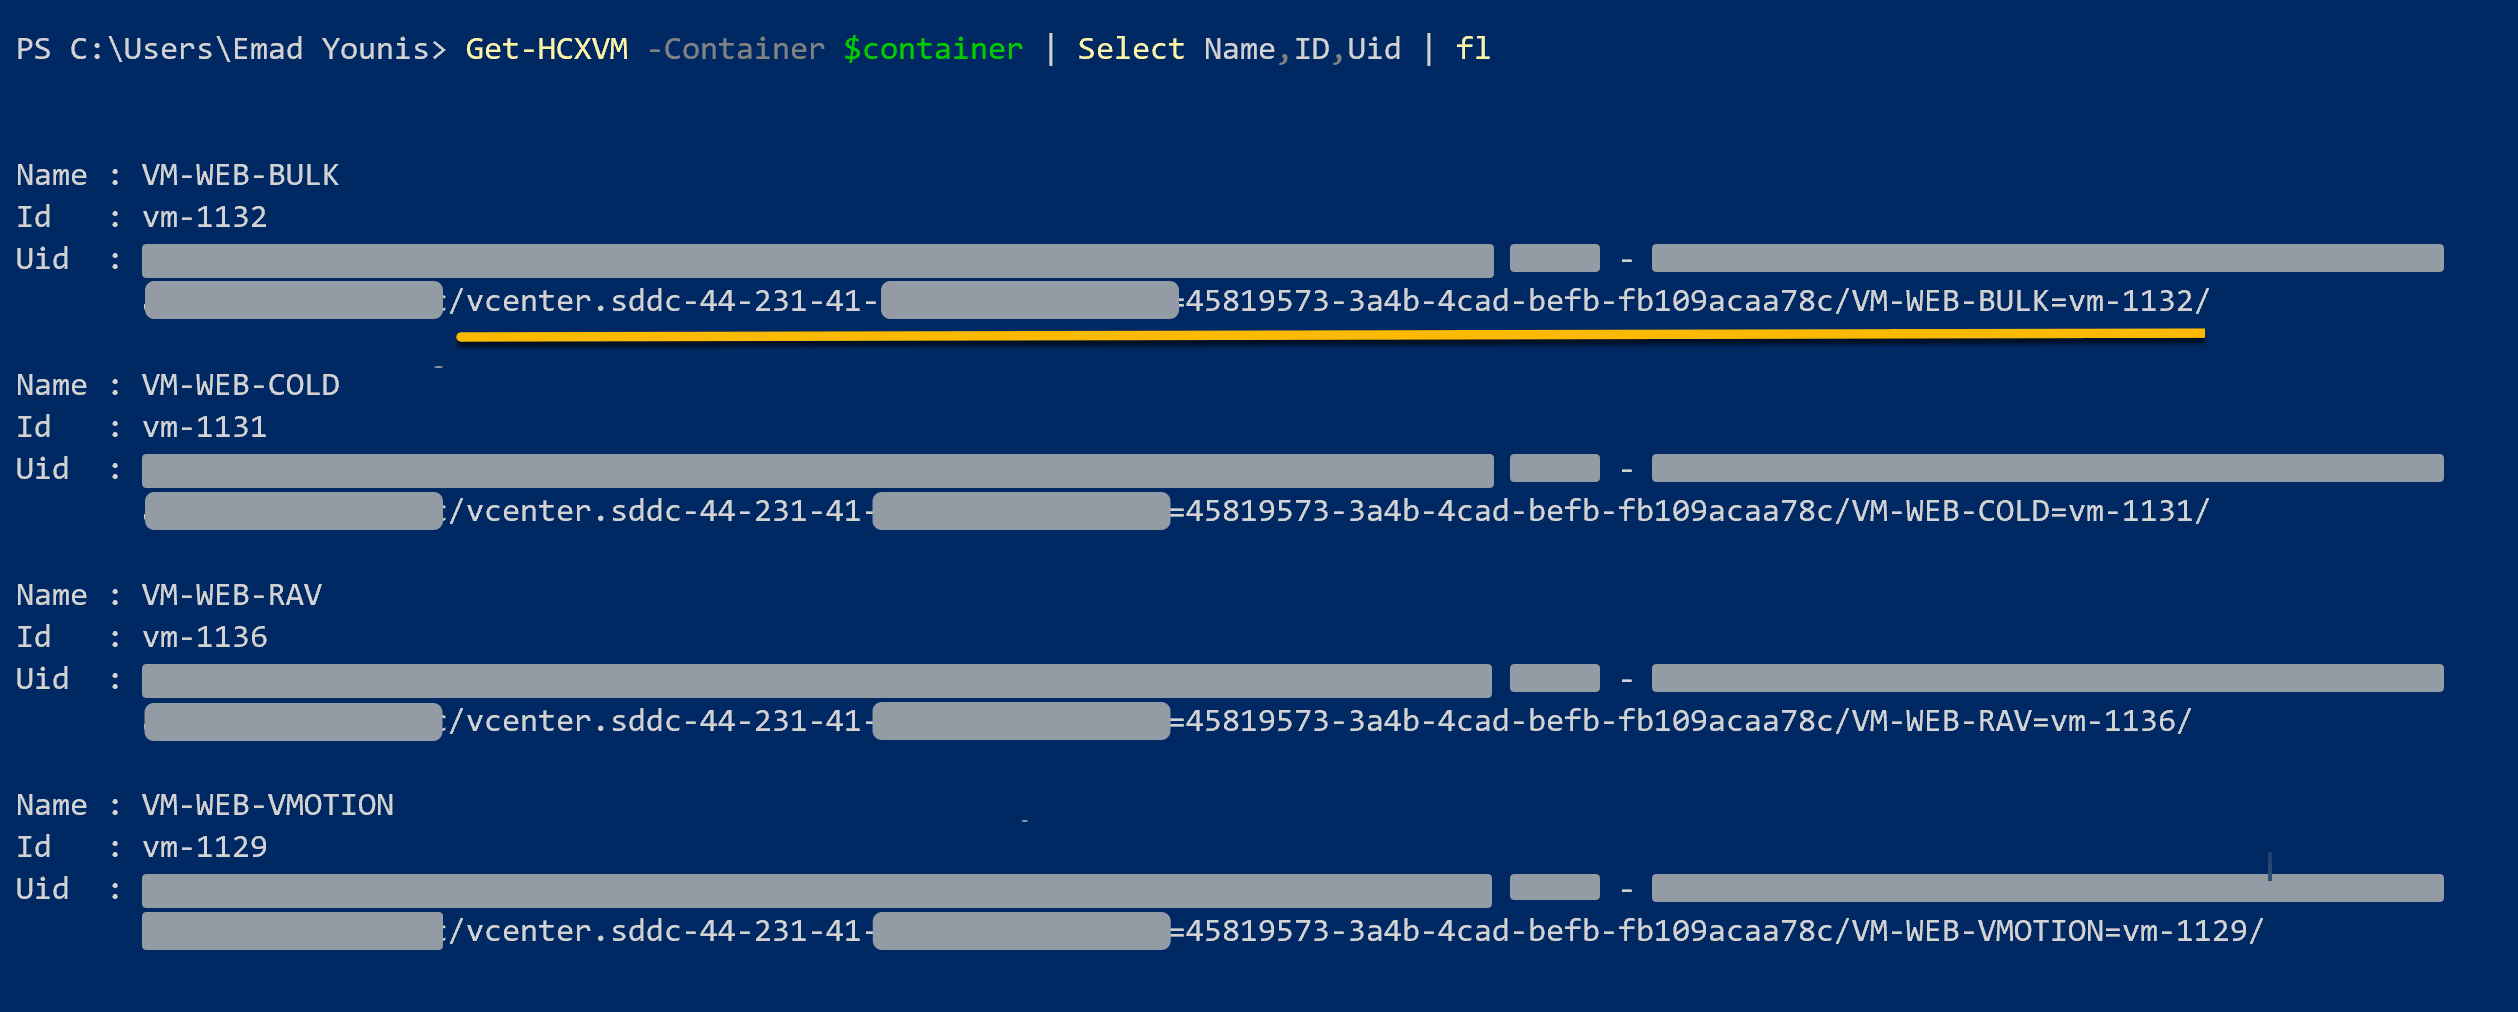
I was also able to pull the destination vCenter Server UUID, VM Name, and VM MoRef ID (HCX has this labeled as Id) using the Get-HCXVM cmdlet.</p>

<p><img src="https://emadyounis.com/assets/img/2020/03/GET-HCXVM.jpg?resize=1024%2C412" alt="" /><br />
HCX removes barriers! These are two distinct vSphere Single Sign-On (SSO) domains between on-prem and VMC, by combining VM instanceUUID with the vCenter Server unique identifier, you can identify VMs across multiple vCenter Servers. Another way to uniquely identify VMs in your environment is the use of vSphere tags. HCX will retain VM tag and category information from the source to the destination vCenter Server, see examples above. Now you can migrate successfully using HCX while understanding the impact on your VMs IDs and solutions that rely on them.</p>]]></content><author><name>Emad Younis</name></author><category term="VMware HCX" /><category term="HCX" /><category term="MoREF ID" /><category term="VM InstanceUUID" /><category term="VMware HCX" /><summary type="html"><![CDATA[I’ve received several questions lately on what happens to a VM’s Managed Object Reference (MoRef) ID and InstanceUUID when it’s migrated across different vCenter Servers using VMware HCX. This information is essential for anything being used to identify VMs, such as provisioning systems, CMDBs, ticketing systems, and backup solutions are examples of tooling using this information.]]></summary><media:thumbnail xmlns:media="http://search.yahoo.com/mrss/" url="https://emadyounis.com/assets/img/2020/03/HCX-VM-IDs-Feature-Image.jpg" /><media:content medium="image" url="https://emadyounis.com/assets/img/2020/03/HCX-VM-IDs-Feature-Image.jpg" xmlns:media="http://search.yahoo.com/mrss/" /></entry><entry><title type="html">The Next Chapter</title><link href="https://emadyounis.com/the-next-chapter/" rel="alternate" type="text/html" title="The Next Chapter" /><published>2019-12-18T10:43:05-08:00</published><updated>2019-12-18T10:43:05-08:00</updated><id>https://emadyounis.com/the-next-chapter</id><content type="html" xml:base="https://emadyounis.com/the-next-chapter/"><![CDATA[<p>Time is truly precious. With a blink of an eye, the years seem to be flying by, which makes it hard to believe in about another month marks four years at VMware for me. Its been a place with no shortage of learning and growing opportunities. I also feel incredibly blessed to have gotten the chance to work and collaborate with so many talented folks across the different business units within VMware.</p>

<p>I spent the first three years working alongside a group of highly-skilled technical marketing architects in the Cloud Platform business unit (CPBU), part of the R&amp;D organization at VMware. My first focus area was vCenter Server, a product I was familiar with and used as a customer. I started out helping customers migrate from vCenter Server for Windows to the vCenter Server Appliance (VCSA) and covering the vCenter Server product overall. We did these migrations using various methods with no to minimal downtime, depending on the customer environment. Of course, this was before the release of the first official migration tool, vCenter Server 6.0 U2m, announced during VMworld 2016.</p>

<p>Once the official vCenter Server migration tool was available, it made sense to also focus on vSphere lifecycle. The vCenter Server migration tool not only copied data (inventory and configuration by default) from one platform to another (vCenter Server for Windows to the VCSA), the process was also an upgrade. During this time, I worked on a series of content that included scenarios and later an ebook to help customers with their vSphere upgrades. Adam Eckerle and I also started to create workshops that we delivered at various VMUGs, VMworld US, and VMworld EMEA. These workshops became in such high demand; this led to the creation of a team under the vSphere Tech Marketing managed by Adam to specifically help with vSphere lifecycle.</p>

<p>Shortly after, in addition to vCenter Server, I started working on VMware Cloud on AWS (VMC) with a focus on hybridity and workload mobility. It was exciting being part of something like VMC from the beginning and getting the opportunity not only to influence the service but also work on new technology such as stretched clusters and hybrid linked mode. When it came to workload mobility, this was my first introduction to VMware HCX. An all-in-one platform that simplified workload mobility from any site, whether on-premises or cloud. Around this time, I had been in technical marketing for about 2 1/2 years and began to think about what I wanted to do next in my career.</p>

<p>An opportunity to join the vSphere product management team presented itself working on driving the direction for vCenter Server lifecycle. Towards the end of 2018, I joined the PM team working on new functionality to help simplify vSphere lifecycle. While I can’t go into details, I would recommend watching this <a href="https://s3.us-east-2.amazonaws.com/vmworld-europe-2019/HBI1973BE.mp4">VMworld session</a> presented by William Lam and myself and pay attention to the tech preview section. Having been in the PM role for a year, I learned so much about product development, delivery, and the number of meetings one could have on their calendar.</p>

<p>Recently another opportunity presented itself, and I’m excited to announce that I have joined the VMware HCX team as Customer Zero. In this role, I’ll be working closely with VMware HCX product management, engineering, and design on upcoming enhancements/functionality and also providing early feedback on usability and integrations, including on-premises, VMware Cloud on AWS, Google Cloud VMware Solution, and Azure VMware Solution. There is also the bonus of getting to work with a community member and food thief (guard your plate), Amy Lewis. I look forward to this new opportunity and sharing everything coming from the VMware HCX team.</p>]]></content><author><name>Emad Younis</name></author><category term="Blog" /><summary type="html"><![CDATA[Time is truly precious. With a blink of an eye, the years seem to be flying by, which makes it hard to believe in about another month marks four years at VMware for me. Its been a place with no shortage of learning and growing opportunities. I also feel incredibly blessed to have gotten the chance to work and collaborate with so many talented folks across the different business units within VMware.]]></summary><media:thumbnail xmlns:media="http://search.yahoo.com/mrss/" url="https://emadyounis.com/assets/img/2019/12/Next-Chapter.png" /><media:content medium="image" url="https://emadyounis.com/assets/img/2019/12/Next-Chapter.png" xmlns:media="http://search.yahoo.com/mrss/" /></entry><entry><title type="html">vCenter Server 6.7 Update 1 Convergence Tool</title><link href="https://emadyounis.com/vcenter-server-6-7-update-1-convergence-tool/" rel="alternate" type="text/html" title="vCenter Server 6.7 Update 1 Convergence Tool" /><published>2018-10-22T07:29:58-07:00</published><updated>2018-10-22T07:29:58-07:00</updated><id>https://emadyounis.com/vcenter-server-6-7-update-1-convergence-tool</id><content type="html" xml:base="https://emadyounis.com/vcenter-server-6-7-update-1-convergence-tool/"><![CDATA[<p>The embedded deployment is now VMware’s recommended deployment model for vCenter Server. This means all the required vCenter Server services are running on the same node. The release of <a href="http://emadyounis.com/whats-new-in-vcenter-server-6-7-update-1/">vSphere 6.7 Update 1 introduces the convergence CLI tool</a>. Customers with an existing external deployment can now change their topology to embedded. This deployment model also supports Enhanced Linked Mode (ELM). In the past, an external Platform Services Controller (PSC) was only needed for ELM. This is no longer the case with a simplified deployment model. While we are on the subject, let me clear up a few misconceptions I’ve seen about embedded deployments.</p>

<ul>
  <li>The first misconception is an embedded deployment is a new deployment model. The embedded deployment model is not a new concept. It has been around since the initial VirtualCenter (2004) deployment. Over time VMware introduced new vCenter Server services including the PSC. With the addition of the PSC services, the embedded deployment model did not support ELM. Greenfield deployments on vSphere 6.5 and 6.7 support embedded deployments with ELM.</li>
  <li>Another misconception is the maximums supported differs between the two deployment models. The embedded deployment supports the same vCenter Server maximums as the external deployment. This includes the same number of hosts, VMs, datastores, etc. there is no difference. Also, the embedded deployment supports a total of 15 vCenter Servers in a vSphere SSO domain.</li>
  <li>A third misconception is with a PSC failure, an embedded deployment is likely to fail. A PSC failure, whether external or embedded, has the same result. Users will no longer be able to authenticate to the registered vCenter Server(s). The probability of PSC service failing when embedded is slim. Using vCenter Server High Availability (VCHA) is the preferred method for protecting against these types of failures. This also removes the overhead of using a load balancer for PSC high availability.</li>
</ul>

<h2 id="convergence-tool-overview">Convergence Tool Overview</h2>

<p>[<span style="color: #ff0000;"><strong>Update:</strong></span> The vCenter Server Appliance convergence tool is now also included in <a href="https://docs.vmware.com/en/VMware-vSphere/6.5/rn/vsphere-vcenter-server-65u2d-release-notes.html">vCenter Server Update 2d</a>. Same steps below apply]</p>

<p>The convergence tool is only available on the vCenter Server Appliance (VCSA) 6.7 Update 1 ISO. If you are familiar with the VCSA lifecycle JSON templates, the converge CLI tool is similar. There are two JSON templates, converge and decommission. In an external deployment, the PSC is running on a separate node. The necessary PSC RPMs are not installed on the registered vCenter Server. The converge tool will handle the installation of the PSC RPMs on the vCenter Server. There is no manual intervention required and it does not make any changes to the external PSC. After the installation of the PSC, it then registers with the vCenter Server.</p>

<p>Next is the replication of the vSphere SSO data from the external PSC to the embedded PSC. The PSC replication partner is part of the converge tool JSON template, more on that in a bit. Only during convergence is replication from an external PSC to embedded PSC supported. Once the replication is complete, it time to decommission the external PSC. Let’s walk through the steps in more detail.</p>

<p><strong><span style="color: #ff0000;">Note:</span></strong> The convergence process can only run on one VCSA at a time.</p>

<h2 id="prerequisites">Prerequisites</h2>

<p>There are a few prerequisites and considerations before starting the convergence process:</p>

<ul>
  <li>The converge tool only supports the VCSA and PSC 6.7 Update 1. All nodes must be on 6.7 Update 1 before converting.</li>
  <li>If you are currently running a Windows vCenter Server or PSC, you must first migrate to the appliance.</li>
  <li>Before converting take a backup of your VCSA(s) and a least one of the PSCs in your vSphere SSO domain.</li>
  <li>Know all other solutions (i.e. SRM, vROPS, NSX, etc.) using the PSC for authentication in your environment. They will need to be re-registered after the convergence completes and before decommissioning.</li>
  <li>A machine on a routable network which can communicate with the VCSA and PSC will be used to run the convergence and decommission process.</li>
  <li><span style="color: #000000;">It is recommended to change the DRS Automation Level to partially automated or manual and the Migration Threshold to conservative. There could be issues if the VCSA being converged is moved during the process.</span></li>
  <li>If VCHA is enabled, it must be disabled prior to running the convergence process.</li>
  <li>The converge process will handle PSC HA load balancers, make sure you point to the VIP in the JSON template.</li>
  <li>All vSphere SSO data is migrated with the exception of local OS users.</li>
</ul>

<p><strong><span style="color: #ff0000;">Note:</span></strong> If the VCSA File-Based backup is running using the scheduler the convergence process will fail. You must delete the scheduler prior to starting the convergence process. It can be re-enabled after the convergence process is complete.</p>

<h2 id="convergence-steps">Convergence Steps</h2>

<ol>
  <li>Backup all VCSAs and at least one PSC (multi-master) within your vSphere environment.</li>
  <li>Mount the VCSA 6.7 Update 1 ISO on a machine with routable network access to the VCSA and PSC. The VCSA ISO supports macOS, Linux, and Windows.<img src="https://emadyounis.com/assets/img/2018/10/Converge-VCSA-ISO.png?resize=933%2C403" alt="" /></li>
  <li>Expand the vcsa-converge-cli directory and go to templates. Open the converge directory and copy the converge.json file to your local machine.<img src="https://emadyounis.com/assets/img/2018/10/Converge-VCSA-Directory.png?resize=908%2C616" alt="" /></li>
  <li>
    <p>Open the local copy of the coverge.json file with your favorite editor. Fill out the JSON template with the required information. There are two sections to pay close attention to. The first is the “ad_domain_info” section. If your PSC is a member of an active directory domain, this section needs filled out. Otherwise, this entire section is not needed. The second section is the “replication” section of the JSON template. If there is only a single PSC with no replication partners, then this section is not needed. Use the <a href="https://kb.vmware.com/s/article/2127057">vdcrepadmin command</a> to check the replication agreements if you are unsure. <strong><span style="color: #ff0000;">Note:</span></strong> Use ./vcsa-util converge – –template–help for additional help filling out the converge JSON template.</p>

    <div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code><table class="rouge-table"><tbody><tr><td class="rouge-gutter gl"><pre class="lineno">1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
</pre></td><td class="rouge-code"><pre> &lt;pre class="lang:default decode:true"&gt;{
     "__version": "2.11.0",
     "__comments": "Template for VCSA with external Platform Services Controller converge",
         "vcenter": {
             "description": {
                "__comments": [
                     "This section describes the vCenter appliance which you want to",
                     "converge and the ESXi host on which the appliance is running. "
                 ]
             },
             "managing_esxi_or_vc": {
                 "hostname": "esx-02.cpbu.corp",
                 "username": "root",
                 "password": "P@ssw0rd"
             },
             "vc_appliance": {
                 "hostname": "vcsa-01.cpbu.corp",
                 "username": "administrator@vsphere.local",
                 "password": "P@ssw0rd",
                 "root_password": "P@ssw0rd"
             },
             "ad_domain_info": {
                 "__comments": [
                     "Important Note: This section is needed only when PSC (Platform Services Controller) appliance is joined to a domain.",
                     "Remove this section if PSC appliance is not joined to a domain.",
                     "Keeping this section without valid values results in JSON validation errors."
                 ],
                 "domain_name": "cpbu.corp",
                 "username": "emad",
                 "password": "P@ssw0rd",
                 "dns_ip": "192.168.13.50"
         },
     "replication": {
             "description": {
                "__comments": [
                "Important Note: Make sure you provide the information in this section very carefully, as this changes the replication topology.",
                "Refer to the documentation for complete details. Remove this section if this is first converge operation in your setup.",
                "This section provides details of the PSC node which will be set up as a replicated node for a new PSC on the target VCSA node."
             ]
                 },
             "partner": {
                 "hostname": "psc-02.cpbu.corp"
             }
         }
 }
</pre></td></tr></tbody></table></code></pre></div>    </div>

    <p><strong><span style="color: #ff0000;">Note:</span></strong> You can leave the passwords for any of the sections blank in the template and will be prompted during the convergence process.</p>
  </li>
  <li>After completing the converge JSON template, make sure you save it.</li>
  <li>Open a terminal window to the vcsa-util application path. Depending on the local operating system in use will determine the directory. In this example, I’m using macOS and using the vcsa-util under the mac directory.</li>
  <li>Run ./vcsa-util converge – –help to get a list of the supported parameters.<br />
 <img src="https://emadyounis.com/assets/img/2018/10/Converge-VCSA-Util.png?resize=1280%2C323" alt="" /></li>
  <li>To start the convergence process, use the correct parameters followed by the path of the converge JSON template you saved earlier. ```
    <pre class="wrap:true lang:default decode:true">./vcsa-util converge --no-ssl-certificate-verification --backup-taken --verbose /Users/eyounis/Documents/converge.json
 ```
</pre>
  </li>
  <li>Once the convergence process begins, your VCSA will not be available until the process is complete.<img src="https://emadyounis.com/assets/img/2018/10/Converge-Process-Started.png?resize=1234%2C618" alt="" /></li>
  <li>After the convergence process has completed, verify the VCSA is now running with an embedded PSC. There are two ways to verify. The first is using the VMware Appliance Management on port 5480. Go to the Summary tab and verify the type is “vCenter Server with an embedded Platform Services Controller”. A second option is using the vSphere Client (HTML5). Look under the Administration menu for System Configuration and verify the type as above.</li>
  <li>If there are any products using the PSC for authentication they will need to be re-registered. Re-register them with the embedded VCSA deployment before decommissioning the external PSC. Also, do not decommission an external PSC until all VCSAs registered have gone through the convergence process.</li>
</ol>

<h2 id="decommissioning-steps"><strong>Decommissioning Steps</strong></h2>

<p><strong><span style="color: #ff0000;">*Verify the steps above have been completed prior to starting the decommissioning process*</span></strong></p>

<ol>
  <li>Expand the vcsa-converge-cli directory and go to templates. Open the decommission directory and copy the decommission_psc.json file to your local machine.</li>
  <li>Open the local copy of the decommission_psc.json file with your favorite editor. Fill out the JSON template with the required information. If the default port of 443 was changed, make to enter the custom port that was used in the decommission template in the specified sections. ```
    <pre class="wrap:true lang:default decode:true">{
     "__comments": "Template for decommissioning PSC node with converge CLI tool.",
     "__version": "2.11.0",
         "psc": {
             "description": {
                "__comments": [
                    "This section describes the PSC appliance which you want to",
                     "decommission and the ESXi host on which the appliance is running. "
                 ]
             },
             "managing_esxi_or_vc": {
                 "hostname": "esx-02.cpbu.corp",
                 "username": "root",
                 "password": "P@ssw0rd"
             },
             "psc_appliance": {
                 "hostname": "psc-01.cpbu.corp",
                 "username": "administrator@vsphere.local",
                 "password": "P@ssw0rd",
                 "root_password": "P@ssw0rd"
             }
         },
         "vcenter": {
             "description": {
                "__comments": [
                     "This section describes the embedded vCenter appliance which is in ",
                     "replication with the provided PSC"
                 ]
             },
             "managing_esxi_or_vc": {
                 "hostname": "esx-02.cpbu.corp",
                 "username": "root",
                 "password": "P@ssw0rd"
             },
             "vc_appliance": {
                 "hostname": "vcsa-01.cpbu.corp",
                 "username": "administrator@vsphere.local",
                 "password": "P@ssw0rd",
                 "root_password": "P@ssw0rd"
             }
         }
 }
 ```
</pre>
  </li>
  <li>After completing the decommission JSON template, save it.</li>
  <li>Open a terminal window to the vcsa-util application path, same steps as above.</li>
  <li>Run ./vcsa-util decommission – –help to get a list of the supported parameters.</li>
  <li>To start the decommission process, use the correct parameters followed by the path of the decommission JSON template you saved earlier. ```
    <pre class="wrap:true lang:default decode:true ">./vcsa-util decommission --no-ssl-certificate-verification --verbose /Users/eyounis/Documents/decommission_psc.json
 ```
</pre>
  </li>
  <li>The decommissioning process will begin removing the external PSC from the vSphere SSO domain. There are validations included to ensure there are no registered VCSAs to the external PSC being decommissioned. If any are found, the decommissioning process will fail.<br />
 <img src="https://emadyounis.com/assets/img/2018/10/Decommision-Process.png?resize=1189%2C649" alt="" /></li>
</ol>

<h2 id="summary">Summary</h2>

<p>Great job by the vCenter Server engineering team for all their hard work on this tool. As stated earlier VMware’s recommended deployment model going forward is embedded. I would say the writing is on the wall for the external deployment now that the convergence tool is available. The next blog post will cover a few topology convergence examples. Happy converting 🙂</p>]]></content><author><name>Emad Younis</name></author><category term="vCenter" /><category term="VCSA" /><category term="VCSA 6.7" /><summary type="html"><![CDATA[The embedded deployment is now VMware’s recommended deployment model for vCenter Server. This means all the required vCenter Server services are running on the same node. The release of vSphere 6.7 Update 1 introduces the convergence CLI tool. Customers with an existing external deployment can now change their topology to embedded. This deployment model also supports Enhanced Linked Mode (ELM). In the past, an external Platform Services Controller (PSC) was only needed for ELM. This is no longer the case with a simplified deployment model. While we are on the subject, let me clear up a few misconceptions I’ve seen about embedded deployments.]]></summary><media:thumbnail xmlns:media="http://search.yahoo.com/mrss/" url="https://emadyounis.com/assets/img/2018/10/Convergence-Tool-Image.png" /><media:content medium="image" url="https://emadyounis.com/assets/img/2018/10/Convergence-Tool-Image.png" xmlns:media="http://search.yahoo.com/mrss/" /></entry><entry><title type="html">What’s New in vCenter Server 6.7 Update 1</title><link href="https://emadyounis.com/whats-new-in-vcenter-server-6-7-update-1/" rel="alternate" type="text/html" title="What’s New in vCenter Server 6.7 Update 1" /><published>2018-10-16T13:18:55-07:00</published><updated>2018-10-16T13:18:55-07:00</updated><id>https://emadyounis.com/whats-new-in-vcenter-server-6-7-update-1</id><content type="html" xml:base="https://emadyounis.com/whats-new-in-vcenter-server-6-7-update-1/"><![CDATA[<p>Today I’m happy to announce <a href="https://my.vmware.com/en/web/vmware/info/slug/datacenter_cloud_infrastructure/vmware_vsphere/6_7">vSphere 6.7 Update 1</a> is now generally available. This release includes a single vSphere Client to manage them all. I’m referring to the HTML5 based vSphere Client, now fully featured. Also, included in this release are the necessary tools for convergence and repointing. An external Platform Services Controller (PSC) for enhanced linked mode is a thing of the past. Customers can now convert to a simplified embedded deployment supporting the same functionality.</p>

<p>The vSphere SSO domain also is receiving more flexibility with support for embedded repointing. Now a single embedded deployment can move to another vSphere SSO domain. Another feature with enhancements in vSphere 6.7 Update 1 is Content Library. It now supports native vCenter Server templates (.vmtx) and Open Virtual Appliance (OVA). Of course, there are more new features and enhancements in this release. Without further ado, here is what’s new in vCenter Server 6.7 Update 1.</p>

<h2 id="vsphere-client">vSphere Client</h2>

<p>The wait is finally over! We now have a fully featured vSphere client in vSphere 6.7 Update 1. Delivering a fully featured client to customers was only part of the process. The vSphere team also wanted to optimize the vSphere Client’s performance and workflows. Ensuring the best customer experience possible. This release includes smart porting over and completing the remaining features which included:</p>

<ul>
  <li>vCenter High Availability (VCHA)</li>
  <li>Auto Deploy</li>
  <li>Host Profiles</li>
  <li>vSphere Update Manager</li>
  <li>Network Topology Diagrams</li>
  <li>Performance Charts</li>
  <li>Improved Searching</li>
  <li>Dark Theme</li>
  <li>more…<a href="https://www.youtube.com/playlist?list=PLmp0id7yKiEcEzzXTOr2DrThIsPvfn1EX">vSphere Client Youtube Playlist</a></li>
</ul>

<p>There are two features I want to highlight from the vSphere Client in vSphere 6.7 Update 1. The first is the improved searching capabilities. Customers can now search objects with a string and filter based attributes. These attributes include Tags, Custom Attributes, and VM power state to name a few. For common searches, there is also an option to save the search for future usage.</p>

<p><img src="https://emadyounis.com/assets/img/2018/10/HTML5-Search.png?resize=1280%2C332" alt="" /></p>

<p>The second feature I want to highlight is considered one of the top feature requests. The vSphere team has been listening and now the dark theme option is available. Now customers can switch between the traditional light theme to the new dark theme in a single click. When switching to dark theme a blue information banner appears at the top of the screen. In this release dark theme supports vSphere features and plugins. Keep in mind other features and plugins may not render well until the necessary changes are in place. Glad the vSphere team was able to get this nice surprise in this release.</p>

<p><img src="https://emadyounis.com/assets/img/2018/10/HTML5-Dark-Theme-vSphere-Client.png?resize=1280%2C687" alt="" /></p>

<h2 id="convergence-tool">Convergence Tool</h2>

<p>vCenter Server is going back to its roots of a simplified architecture. vSphere 6.0 introduced us to a new vCenter Server service called the PSC. The role of the PSC is to manage the following vSphere SSO domain components:</p>

<ul>
  <li>Authentication</li>
  <li>Licensing</li>
  <li>Tags &amp; Categories</li>
  <li>Global Permissions</li>
  <li>Custom Roles</li>
  <li>Certificates</li>
</ul>

<p>The PSC has two deployment models, embedded and external. The only reason to use an external PSC at the time was for Enhanced Linked Mode (ELM). Otherwise, use the embedded deployment model for simplicity. Starting with vSphere 6.7 and 6.5 Update 2 the embedded deployment model supports ELM, but only for greenfield deployments. Until now customers who deployed an external PSC for ELM had no way to change their topology to an embedded PSC. vSphere 6.7 Update 1 introduces a new CLI tool to converge a PSC deployment from external to embedded.</p>

<p>The convergence tool is available in a directory called “VCSA-Converge-CLI” on the VCSA 6.7 Update 1 ISO. Before using the convergence tool there are two important prerequisites. First, a vSphere environment must be running vSphere 6.7 Update 1. This includes all the external PSCs and vCenter Servers in the vSphere SSO domains. Second, the convergence tool does not support Windows PSCs or vCenters Servers. Meaning migrate to the vCenter Server Appliance (VCSA) you should!</p>

<p><img src="https://emadyounis.com/assets/img/2018/10/Converge.png?resize=1008%2C347" alt="" /></p>

<p>There are two JSON template options, converge and decommission. We start by using the converge JSON which will install the necessary PSC RPMs on the external VCSA. After the PSC service gets registered on the external VCSA, its now converted to embedded. But we’re not done, we still need to replicate the vSphere SSO data between the external PSC and the embedded PSC. This is actually taken care of as part of the JSON template and requires no manual intervention. The final step is to decommission the external PSC using the decommission JSON template. Stay tuned, there will be a more detailed blog post with examples coming soon.</p>

<p><span style="color: #ff0000;"><strong>Note:</strong></span> Embedded PSC is the recommended deployment model for vCenter Server.</p>

<p><img src="https://emadyounis.com/assets/img/2018/10/converge.png?resize=874%2C253" alt="" /></p>

<h2 id="embedded-domain-repoint">Embedded Domain Repoint</h2>

<p>Domain repoint is a feature available in vSphere 6.7 using the cmsso-util CLI command. Customers can repoint an external vCenter Server across a vSphere SSO domain. New in vSphere 6.7 Update 1 is support for embedded deployment domain repoint. Remember the time you selected a new vSphere SSO domain instead of an existing? Leaving you with several single embedded deployment instances. With domain repoint we can now join them to a single vSphere SSO domain. Other use cases are merges or acquisitions, no longer requiring a setup of a new vSphere SSO domain.</p>

<p><img src="https://emadyounis.com/assets/img/2018/10/Domain-Repoint.png?resize=874%2C521" alt="" /></p>

<h2 id="vcenter-high-availability">vCenter High Availability</h2>

<p>vCenter Server native high availability was first introduced in vSphere 6.5. This is an active/passive solution designed to protect against application failure. In this case, it’s protecting the vCenter Server application. In vSphere 6.7 Update 1 vCenter High Availability is an example of a smart port workflow. There is no longer two workflows of basic and advanced, now only one workflow. The new workflow is a three-step configuration:</p>
<ul>
  <li>vSphere SSO credentials for either management vCenter Server or management credentials</li>
  <li>Resource settings for the Passive and Witness nodes including compute, storage, and network</li>
  <li>IP Settings for the Passive and Witness nodes</li>
</ul>

<p><img src="https://emadyounis.com/assets/img/2018/10/VCSA-HA-Main.png?resize=1280%2C800" alt="" /></p>

<p>Also included is auto-creation of the Active node clones to create the Passive and Witness nodes. A prerequisite for auto clone provisioning is entering the vSphere SSO domain credentials. Regardless of its self-managed or managed by another vCenter Server. Other enhancements including auto-detection of VCHA during an upgrade. Customers no longer have to destroy a VCHA configuration before upgrading to vSphere 6.7 U1. The upgrade wizard is aware of the configuration and will handle it as part of the upgrade process. We’ll save the best for last, REST APIs for VCHA are also included in the VCSA 6.7 Update 1 API Explorer.</p>
<p><img src="https://emadyounis.com/assets/img/2018/10/VCHA-APIs.png?resize=1280%2C720" alt="" /></p>

<h2 id="content-library">Content Library</h2>

<p>This feature has been around since vSphere 6.0 and is one of my favorites. As a customer, I had to manage several images, scripts, OVAs, and templates for several remote sites. Having to maintain and update the same content in several locations can be a nightmare. Content Library is a native vCenter Server service which solves this problem. It uses the subscriber/publisher model to distribute content. There are two deployment models when using Content Library:</p>

<ul>
  <li>Single vCenter Server managing several sites
    <ul>
      <li>Centralized managed content</li>
      <li>Uses WAN to sync content, requires publishing vCenter Server to be available</li>
      <li>Content stored on a datastore at the remote sites</li>
      <li>When provisioning content at the remote sites, traffic is kept local</li>
    </ul>
  </li>
  <li>Multi vCenter Server
    <ul>
      <li>Centralized managed content</li>
      <li>Uses WAN to sync content</li>
      <li>Can sustain publishing vCenter Server failure, remote locations continue to operate</li>
      <li>Content stored on a datastore at the remote sites</li>
      <li>When provisioning content at the remote sites, traffic is kept local</li>
    </ul>
  </li>
</ul>

<p>This release Content Library now supports two more new file formats. This functionality is already available to VMware Cloud on AWS customers. Now it’s making its way to on-premises vSphere customers in vSphere 6.7 Update 1. Customers can now manage their templates on the local vCenter Server Content Library. Replication of template files to other subscriber Content Libraries is not available in this release. The other new supported format is Open Virtual Appliance (OVA). When importing an OVA file format in a Content Library, its content is first extracted. This allows Content Library to validate the OVA manifest and certificate. After the validation process is complete, it creates an OVF item for deployment. Give Content Library a try in your environment and let us know your thoughts.</p>

<p><img src="https://emadyounis.com/assets/img/2018/10/Content-Library.png?resize=1280%2C380" alt="" /></p>

<h2 id="vsphere-health">vSphere Health</h2>

<p>This is a new feature with huge potential. When deploying your vCenter Server there is an option to enable CEIP. It stands for Customer experience improvement program. When enabled data gets sent to VMware’s analytics cloud, customer workload data is not part of the data collected. This is all anonymous, data is secure and housed in VMware’s data centers. VMware uses this telemetry data to help improve features and customer experience. Now when enabled this functionality provides even more value to the customers. It provides an assessment of the vSphere environment and returns KBs on how to solve the problem at hand. For example, the warning you get when you only have a single management network for your ESXi hosts. We detect and provide alarms for both existing and potential problems. This helps in protecting customer environments from future problems.</p>

<p>Keep in mind this is a new service and will not have all health checks day one. The good news is this services independent of the vSphere release cycle. It features an out-of-band delivery infrastructure. If you are running vSphere 6.7 you also have the same capabilities as well. The goal here is overtime this service will become more proactive to ensure you have a healthy vSphere environment. If you haven’t enabled CEIP during your vSphere deployment, it’s easy enough to enable and gain the new benefits this service has to offer.</p>

<p><img src="https://emadyounis.com/assets/img/2018/10/vSphere-Health.png?resize=1280%2C595" alt="" /></p>

<h2 id="appliance-management">Appliance Management</h2>

<p>The appliance management interface (VAMI) continues to gain new functionality with every release. vSphere 6.7 Update 1 continues to add-on from what vSphere 6.5 started. In this release, there is a new tab called “Firewall”. Now customers can manage firewall rules on the VCSA from the VAMI. This was previously only available using the VAMI APIs.</p>

<p><img src="https://emadyounis.com/assets/img/2018/10/VCSA-Firewall-.png?resize=1280%2C720" alt="" /></p>

<p>Another new feature which isn’t obvious is the ability to login VAMI with a local SSO user account. This release supports local vSphere SSO users who are members of the “SytemConfiguration.Administrators group. Also, members of the “Systemonfiguration.BashShellAdministrators” can use their SSO account to log in the VCSA bash shell. This makes it easier from a security perspective to track who logged in and what they did.</p>

<p><img src="https://emadyounis.com/assets/img/2018/10/VAMI-Configurations.png?resize=1280%2C695" alt="" /></p>

<h2 id="summary">Summary</h2>

<p>As you can see vSphere 6.7 Update 1 is full of new features and enhancements for vCenter Server. We will go into more details on these new vCenter Server features and enhancements in future posts. Also, if you have any feedback on the new features or enhancements, please don’t hesitate to reach out.</p>]]></content><author><name>Emad Younis</name></author><category term="vCenter" /><category term="VCSA" /><category term="VCSA 6.7" /><summary type="html"><![CDATA[Today I’m happy to announce vSphere 6.7 Update 1 is now generally available. This release includes a single vSphere Client to manage them all. I’m referring to the HTML5 based vSphere Client, now fully featured. Also, included in this release are the necessary tools for convergence and repointing. An external Platform Services Controller (PSC) for enhanced linked mode is a thing of the past. Customers can now convert to a simplified embedded deployment supporting the same functionality.]]></summary><media:thumbnail xmlns:media="http://search.yahoo.com/mrss/" url="https://emadyounis.com/assets/img/2018/10/VCSA-6.7-Update-1-Blog-Feature-Image.png" /><media:content medium="image" url="https://emadyounis.com/assets/img/2018/10/VCSA-6.7-Update-1-Blog-Feature-Image.png" xmlns:media="http://search.yahoo.com/mrss/" /></entry><entry><title type="html">Learning Hybrid Cloud Extension (HCX) Part 2: Migration Types</title><link href="https://emadyounis.com/learning-hybrid-cloud-extension-hcx-part-2-migration-types/" rel="alternate" type="text/html" title="Learning Hybrid Cloud Extension (HCX) Part 2: Migration Types" /><published>2018-10-08T12:50:03-07:00</published><updated>2018-10-08T12:50:03-07:00</updated><id>https://emadyounis.com/learning-hybrid-cloud-extension-hcx-part-2-migration-types</id><content type="html" xml:base="https://emadyounis.com/learning-hybrid-cloud-extension-hcx-part-2-migration-types/"><![CDATA[<p>I recently attended a cloud migration session. The first thing the speaker said was “we want you to migrate to the Cloud, but we don’t care how you do it”. There was no discussion of service level agreements (SLA), dependencies, or migration options, only get to the cloud! Before migrating any workload, it’s important to have a good understanding of its SLAs, dependencies, and data. Once you have a good grasp of the workload, the next step is selecting the right migration tool or type. The following is in no particular order, but here are a few things to consider before starting a migration:</p>

<ul>
  <li>How will the workloads get migrated?</li>
  <li>Does the migration type meet the SLA of the workloads?</li>
  <li>What is the impact of the migration to the workloads (downtime)?</li>
  <li>Are there any required changes pre and post-migration?</li>
  <li>Is the proper networking (secure) in place and is there enough bandwidth?</li>
  <li>Was a discovery of the environment done, including mapping of dependencies?</li>
</ul>

<p>As you start to ask these questions more will come up. The point is you can’t migrate to the Cloud without understanding the impact. The <a href="http://emadyounis.com/learning-hybrid-cloud-extension-hcx-part-1-overview/">first blog post</a> of this series was an overview of Hybrid Cloud Extension (HCX). This post will focus on the available migration types HCX offers.</p>

<h2 id="migration-types">Migration Types</h2>

<p>HCX supports four different migration types:</p>

<ul>
  <li>Cold Migration – offline</li>
  <li>vMotion (live) – no downtime</li>
  <li>Bulk Migration – low downtime</li>
  <li>Cloud Motion with vSphere Replication – no downtime</li>
</ul>

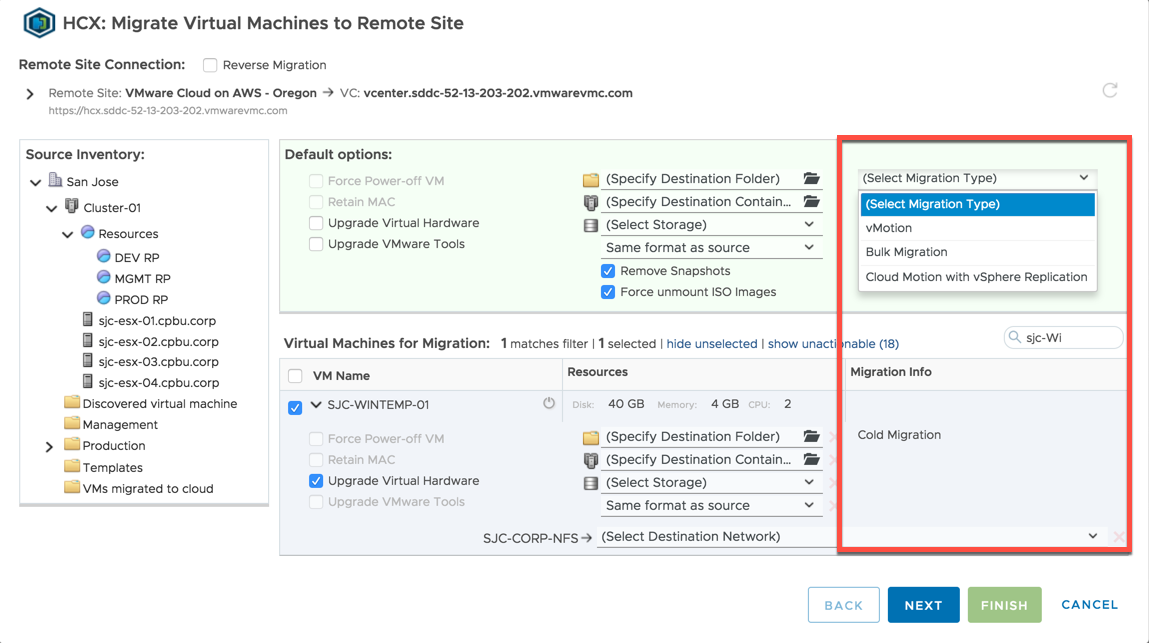
<p>Cold migration and vMotion should be familiar to those using the built-in vSphere mobility options. Bulk Migration and Cloud Motion with vSphere Replication are new options and only available with HCX. Let’s take a look at how each option works and what is the impact to the workloads.</p>

<p><img src="https://emadyounis.com/assets/img/2018/10/Migration-Types-of-HCX.png?resize=1149%2C643" alt="" /></p>

<h2 id="cloud-motion-with-vsphere-replication">Cloud Motion with vSphere Replication</h2>

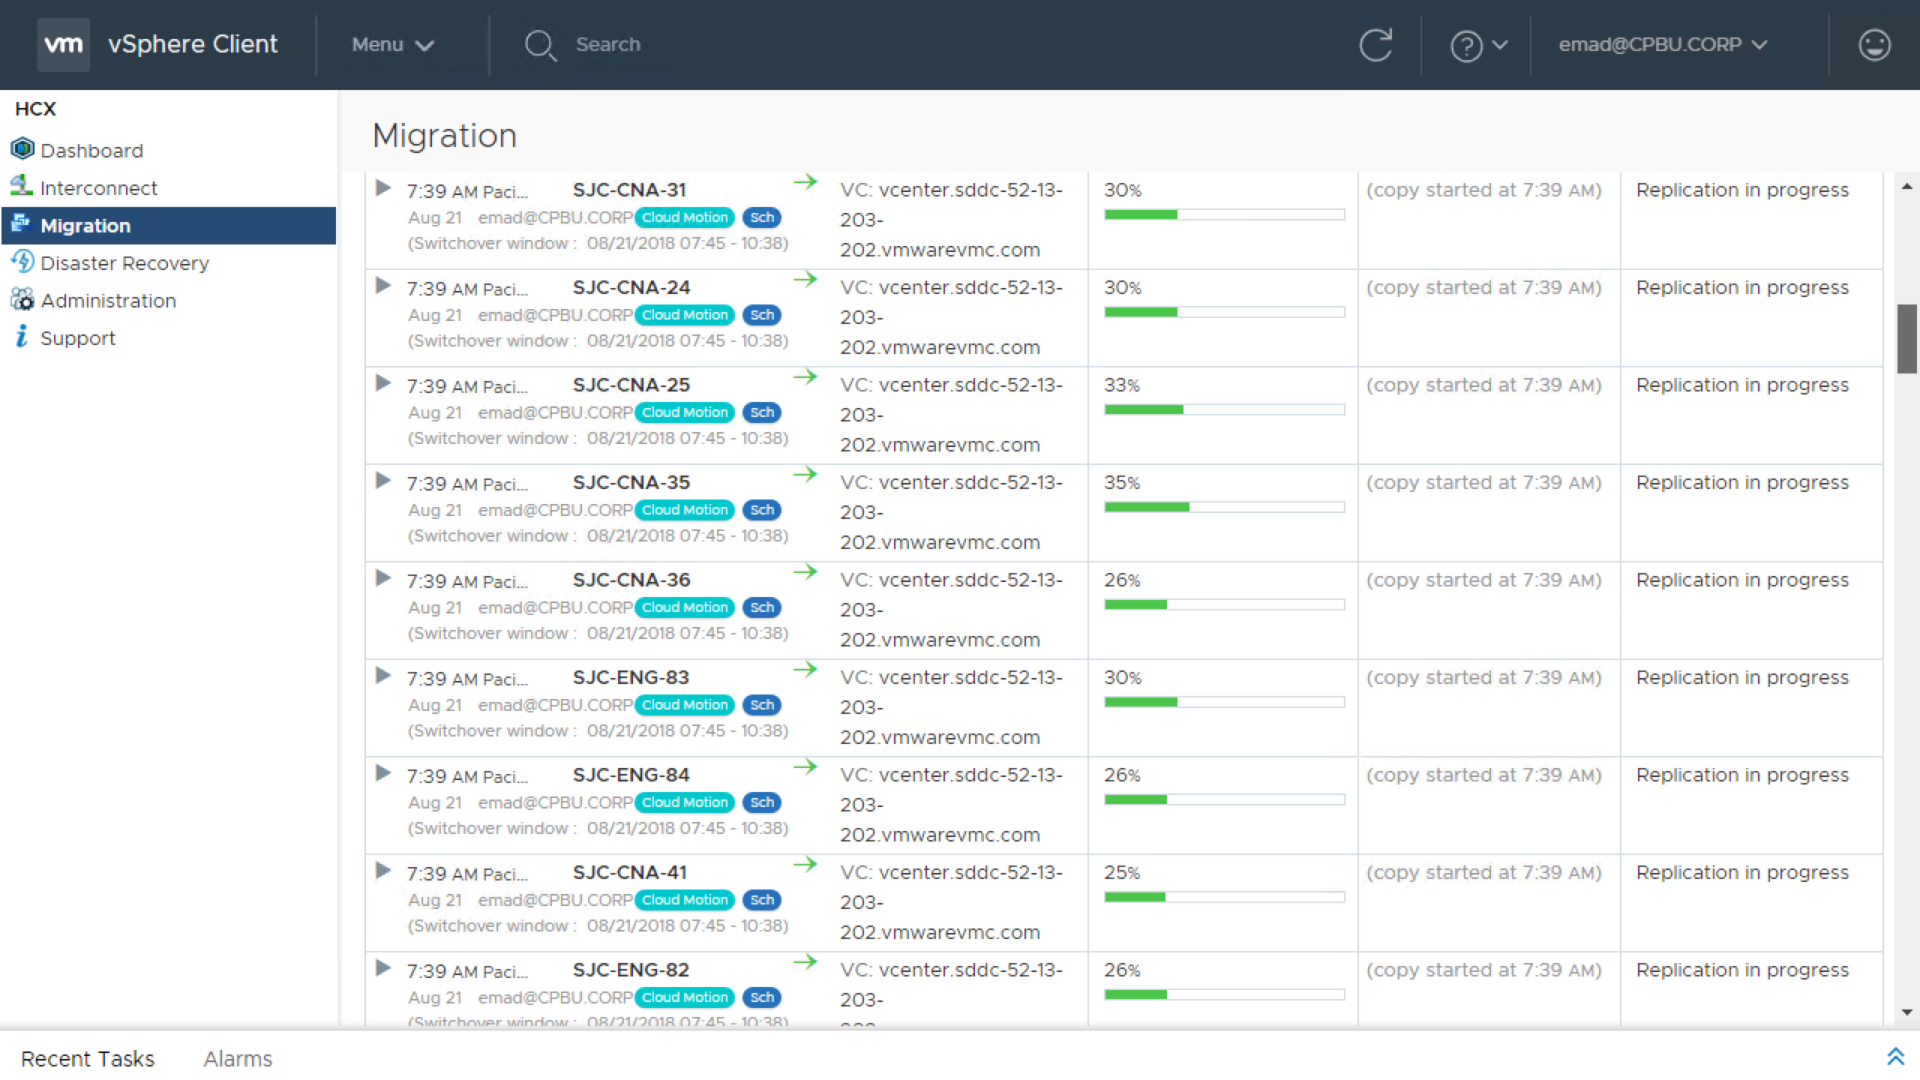
<p>The new kid on the block announced during the VMworld 2018 US keynote. This new option provides zero downtime for workload mobility from source to destination. First, the workload disk(s) (VMDK) get replicated to the destination site. The replication is handled using the HCX built-in vSphere replication. This process is dependent on the amount of data and available network bandwidth. Once the data sync is complete the HCX switchover initiates a vMotion. The vMotion migrates the workload to the destination site and synchronizes only the remaining data (delta) and workload memory state. There is an option to schedule a maintenance window for the vMotion data sync switchover otherwise, it happens immediately.</p>

<p>When using the scheduling option, there are a few things to be aware of. First, the switchover can be re-scheduled any time prior to the actual scheduled time. Secondly, if the initial vSphere Replication data sync has not completed prior to the scheduled window, the workload(s) being migrated will fail. In this case, these workload migrations must be restarted in their entirety. Finally, if the vSphere Replication data sync has completed prior to the scheduled switchover window, HCX will continue to sync delta information to keep the migrated data as current as possible prior to the vMotion switchover. The vMotion switchover happens in a serialized fashion, only one at a time. Today Cloud Motion with vSphere Replication is uni-directional from on-premises to VMware Cloud on AWS (VMC). This is due to HCX leveraging changes in the newer vSphere platform available in VMC. As a result, only VMware Cloud on AWS supports Cloud Motion with vSphere Replication today. Stay tuned, more will be coming for on-premises to on-premises migrations using Cloud Motion with vSphere Replication.</p>

<h4 id="cloud-motion-with-vsphere-replication-notes"><span style="color: #0000ff;"><strong>Cloud Motion with vSphere Replication Notes</strong></span></h4>

<ul>
  <li>Uni-directional from on-premises to VMware Cloud on AWS (see details above)</li>
  <li>Supports source vSphere (vCenter Server / ESXi) versions 5.5 and above</li>
  <li>Cross-version migration from vSphere 5.5 to the current release of 6.7 Update 1</li>
  <li>Currently no support for on-premises to on-premises migrations</li>
  <li>Concurrent migrations = 100 (initial data sync using vSphere Replication)</li>
</ul>

<p><img src="https://emadyounis.com/assets/img/2018/10/Cloud-Motion.png?resize=1920%2C1080" alt="" /></p>

<p><img src="https://emadyounis.com/assets/img/2018/10/VMC-Cloud-Motion.png?resize=1920%2C1080" alt="" /></p>

<h2 id="bulk-migration">Bulk Migration</h2>

<p>Bulk Migration creates a new virtual machine on the destination site. This can either be on-premises or VMC and retains the workload UUID. Then it uses vSphere Replication to copy a snapshot of the workload from source to destination site while the workload is still powered on. In this case, a snapshot is a point of the time of the workload disk state, but not a traditional vSphere snapshot. The Bulk Migration is managed by the HCX interconnect cloud gateway proxy. We’ll go into more details about the HCX interconnect cloud gateway in the deployment post. During the data sync, there is no interruption to the workloads. The data sync is dependent on the amount of data and available bandwidth. There is an option to schedule a maintenance window for the switchover (similar to the schedule options described in the Cloud Motion section above) otherwise, the switchover happens immediately. Once the initial data sync completes, a switchover takes place (unless scheduled). The source site workloads are quiesced and shut down leveraging VMware Tools. If VMware Tools is not available, HCX will prompt you to force power off the workload(s) to initiate the switchover. During the switchover process, a delta sync occurs based on changed block tracking (CBT) to sync the changes since the original snapshot. The workloads on the destination site will begin to power on once the data sync is complete (including delta data changes). There are checks in place to ensure resources are available to power on the workloads. If a destination workload cannot power on due to resources, the source workload will get powered back on.</p>

<p>Unlike cold migration, the downtime incurred after the bulk migration cut over is low. The HCX manager renames the original source workloads by appending a binary timestamp. A migrated VMs folder gets created in the VM and templates view. Finally, the original source workloads get placed in the migrated VMs folder. This also provides an option for easy rollback and quick data seeding since bulk migration supports reverse migrations. One thing worth mentioning is HCX has built-in network resiliency and will pick up where it left off during a data sync if there is any network interruption. On the flip side, if there is an issue powering on workloads on the destination site or missed scheduling a cut over, the entire data sync process will need to be started over. <strong>This technology allows a workload migration between different chipset versions (e.g.</strong> Sandy Bridge to Skylake) and across different CPU families (e.g. AMD to Intel).</p>

<h4 id="bulk-migration-notes"><span style="color: #0000ff;"><strong>Bulk Migration Notes</strong></span></h4>

<ul>
  <li>Automatic update of VM compatibility (hardware) version and VMware Tools available during the switchover</li>
  <li>Supports vCenter Server 5.1 and above / ESXi 5.0 and above</li>
  <li>Cross-version migration from vSphere 5.0 / 5.1 to the current release of 6.7 Update 1</li>
  <li>Concurrent migrations = 100</li>
  <li>Bi-directional migration (reverse HCX option)</li>
</ul>

<h2><img src="https://emadyounis.com/assets/img/2018/10/Bulk-Migration.png?resize=1280%2C720" alt="" /></h2>

<h2 id="vmotion-live-migration">vMotion “Live Migration”</h2>

<p>HCX supports the vMotion we know and love today. The workloads are migrated live with no downtime similar to Cloud Motion with vSphere Replication. vMotion should not be used to migrate hundreds of workloads or workloads with large amounts of data. Instead, use Cloud Motion with vSphere Replication or Bulk Migration. Usually, a vMotion network needs to be configured and routed to the target vSphere host, in this case, the vMotion traffic is handled by the HCX Interconnect cloud gateway for cross-cloud vMotion. vMotion through HCX encapsulates and encrypts all traffic from source to destination removing network complexity of routing to cloud. The vMotion captures workload:</p>

<ul>
  <li>Active Memory</li>
  <li>Execution State</li>
  <li>IP Address</li>
  <li>MAC address</li>
</ul>

<p>HCX has a built-in option to retain the workloads MAC address. If this option is not checked, the workloads will have a different MAC on the destination site. Workloads must be at compatibility (hardware) version 9 or greater and 100 Mbps or above of bandwidth must be available. With vMotion and bi-directional migration, it’s important to consider Enhanced vMotion Compatibility (EVC). The good news here is HCX also handles EVC. The workloads can be migrated seamlessly and once rebooted will inherit the CPU features from the target cluster. This allows a cross-cloud vMotion between different chipset versions (e.g. Sandy Bridge to Skylake) but within the same CPU family (e.g. Intel). Also, an important thing to note is <strong>vMotion is done in a serialized manner</strong>. Only one vMotion occurs at a time and queues the remaining workloads until the current vMotion is complete.</p>

<h4 id="vmotion-notes"><span style="color: #0000ff;">vMotion Notes</span></h4>

<ul>
  <li>Does not support disk sizes over 2TB and shared VMDK files</li>
  <li>Attached virtual media or ISOs can be removed prior using the HCX global option</li>
  <li>Does not support compatibility (hardware) version 8 or below</li>
  <li>Supports vSphere ESXi Host versions 5.5 and above</li>
  <li>Cross-version migration from vSphere 5.5 to the current release of 6.7 Update 1</li>
  <li>Bi-directional migration (reverse HCX option)</li>
</ul>

<p><img src="https://emadyounis.com/assets/img/2018/10/HCX-vMotion.png?resize=1137%2C630" alt="" /></p>

<h2 id="cold-migration">Cold Migration</h2>

<p>As the name states, a cold migration occurs when a workload is offline. CPU compatibility checks do not apply during a cold migration. During a cold migration, VMware’s Network File Copy (NFC) protocol is used to transfer the workloads from source to destination which includes:</p>

<ul>
  <li>Configuration files including BIOS settings (NVRAM)</li>
  <li>Disks associated with the workload</li>
  <li>Log files</li>
</ul>

<p>Usually, cold migration traffic takes place over the host management network. This traffic type is known as provisioning traffic. Provisioning traffic is not encrypted but uses run-length encoding. Run-length encoding is a simple form of lossless data compression. In the case of HCX, cold migration traffic will get encrypted using <strong>Suite B encryption</strong>. It leverages the same host management network to migrate the data through the HCX vMotion proxy. HCX only displays the cold migration option if the selected workload is not powered on. Although HCX provides the option to multi-select it is still limited. vCenter Server only handles 8 concurrent vMotions (cold and live) at a time. It places the remaining selected workloads in a queue until ready to migrate.</p>

<h4 id="cold-migration-notes"><span style="color: #0000ff;">Cold Migration Notes</span></h4>

<ul>
  <li>If transferring large amounts of data consider using Bulk Migration or Cloud Motion</li>
  <li>vCenter Server templates are good candidates</li>
  <li>Supports vSphere ESXi Host versions 5.5 and above</li>
  <li>Cross-version migration from vSphere 5.5 to the current release of 6.7 Update 1</li>
  <li>Bi-directional migration (reverse HCX option)</li>
</ul>

<p><img src="https://emadyounis.com/assets/img/2018/10/HCX-Clold-Migration.png?resize=875%2C325" alt="" /></p>

<h2 id="summary">Summary</h2>

<p>HCX offers customers several different workload mobility options covering different SLAs and requirements. No reconfiguration of the source or destination sites is necessary to get started. The platform offers built-in encryption, WAN optimization, and <a href="https://docs.vmware.com/en/VMware-NSX-Hybrid-Connect/3.5.1/user-guide/GUID-54E5293B-8707-4D29-BFE8-EE63539CC49B.html">cross-version migration</a> through the HCX interconnects. The HCX service is evolving at a rapid rate, the team is making improvements and adding new functionality on almost a monthly basis. Next, we’ll be diving into how to deploy and configure HCX in VMware Cloud on AWS and on-premises.</p>]]></content><author><name>Emad Younis</name></author><category term="Hybrid Cloud Extension" /><summary type="html"><![CDATA[I recently attended a cloud migration session. The first thing the speaker said was “we want you to migrate to the Cloud, but we don’t care how you do it”. There was no discussion of service level agreements (SLA), dependencies, or migration options, only get to the cloud! Before migrating any workload, it’s important to have a good understanding of its SLAs, dependencies, and data. Once you have a good grasp of the workload, the next step is selecting the right migration tool or type. The following is in no particular order, but here are a few things to consider before starting a migration:]]></summary><media:thumbnail xmlns:media="http://search.yahoo.com/mrss/" url="https://emadyounis.com/assets/img/2018/10/HCX-Migration-Types-Blog-Logo.png" /><media:content medium="image" url="https://emadyounis.com/assets/img/2018/10/HCX-Migration-Types-Blog-Logo.png" xmlns:media="http://search.yahoo.com/mrss/" /></entry><entry><title type="html">Learning Hybrid Cloud Extension (HCX) Part 1: Overview</title><link href="https://emadyounis.com/learning-hybrid-cloud-extension-hcx-part-1-overview/" rel="alternate" type="text/html" title="Learning Hybrid Cloud Extension (HCX) Part 1: Overview" /><published>2018-09-19T15:02:04-07:00</published><updated>2018-09-19T15:02:04-07:00</updated><id>https://emadyounis.com/learning-hybrid-cloud-extension-hcx-part-1-overview</id><content type="html" xml:base="https://emadyounis.com/learning-hybrid-cloud-extension-hcx-part-1-overview/"><![CDATA[<p><a href="https://hcx.vmware.com/#/home">Hybrid Cloud Extension (HCX)</a> is an all in one solution for workload mobility. Customers can freely move workloads between multiple on-premises environments as well as VMware Cloud on AWS (VMC). During the <a href="https://www.youtube.com/watch?v=mjYP2IuZK6k">VMworld US 2018 day 1 keynote</a> there were several demos shown, one included a data center evacuation using HCX (51:57). The data center evacuation was using a new HCX migration type called Cloud Motion with vSphere Replication. I’ll cover the HCX migration types in a later post. The workloads were being migrated from an on-premises data center to VMware Cloud on AWS (VMC). The big deal here is the impact during the migration to the users was NONE, ZIP, ZERO downtime. And there was also no replatforming of the workloads or applications.</p>

<p><img src="https://emadyounis.com/assets/img/2018/09/HCX-Dashboard.png?resize=1280%2C768" alt="HCX Dashboard" title="HCX Dashboard" /></p>

<p>Think about what’s usually involved when migrating workloads from one location to another. The network is at the top of the list, ensuring adequate bandwidth and routing is in place. Not only from data center to data center or data center to cloud, but also across regions and remote sites. Validating vSphere version compatibility between the source and destination is also important. Other workload migration considerations could include:</p>

<ul>
  <li>Moving across different vSphere SSO domains independent of enhanced linked mode</li>
  <li>Mapping workload dependencies</li>
  <li>Older hardware preventing from upgrading to vSphere 6.x</li>
  <li>Bi-directional migrations independent of vSphere SSO domains, vSphere versions, hardware, or networks</li>
  <li>Validation of resources (compute and storage) on the destination side</li>
  <li>SLA and downtime involved</li>
  <li>Mobility options correlating to SLAs (downtime, low downtime, no downtime)</li>
  <li>No replatforming of the workloads or applications including no changes to IP or MAC Addresses, VM UUID, certs</li>
</ul>

<p>These are only a few examples of workload migration considerations, but you get the point. I’ve been working with the HCX team for the past few months and I have to say it’s definitely great technology. They have built-in the necessary tooling within the product and removed several boundaries.</p>

<h2 id="hcx-overview">HCX Overview</h2>

<p>HCX is the swiss army knife of workload mobility. It abstracts and removes the boundaries of underlying infrastructure focusing on the workloads. A HCX vMotion, for example, requires no direct connectivity to ESXi hosts in either direction compared to a vSphere vMotion. All HCX vMotion traffic gets managed through the HCX vMotion Proxy at each location. The HCX vMotion Proxy resembles an ESXi host within the vCenter Server inventory. It’s deployed at the data center level by default, no intervention is necessary. One thing to mention is the HCX vMotion proxy gets added to the vCenter Server host count by default. The HCX team is aware and will be changing this in the future, but this has no impact on your vSphere licensing.</p>

<p><img src="https://emadyounis.com/assets/img/2018/09/HCX-Proxy.png?resize=1280%2C768" alt="HCX vMotion Proxy" title="HCX vMotion Proxy" /></p>

<p>Another boundary HCX removes is it supports several versions of vSphere going back to vSphere 5.0 to the most current release of vSphere 6.7 Update 1. This provides flexibility in moving workloads across vSphere versions, on-premises locations, and vSphere SSO domains. For on-premises to on-premises migrations, a <a href="https://www.vmware.com/products/nsx-hybrid-connect.html">NSX Hybrid Connect license</a> is required per HCX site pairing. We will cover site pairing in the configuration blog post. Migrating workloads from on-premises to VMC does not require a separate HCX license. By default when deploying a VMC SDDC HCX is included as an add-on and is enabled by default. From the VMC add-ons tab, all that is required is clicking open Hybrid Cloud Extension and then deploy HCX. The deployment of HCX is completely automated within the VMC SDDC.</p>

<p><img src="https://emadyounis.com/assets/img/2018/09/HCX-Interconnect-Components.png?resize=1280%2C769" alt="HCX Components" title="HCX Components" /></p>

<p>In order to start migrating workloads, network connectivity between the source and destination needs to be in place. The good news is it’s all built-in to the product. HCX has WAN optimization, deduplication, and compression to increase efficiency while decreasing the time it takes to perform migrations. The minimum network bandwidth required to migrate workloads with HCX is 100 Mbps. HCX can leverage your internet connection as well as direct connect. The established network tunnel is secured using suite B encryption. The on-premises workloads being migrated with no downtime will need to reside on a vSphere Distributed Switch (VDS). It also supports a 3rd party switch in the Nexus 1000v. Cold and bulk HCX migration types are currently the only two options which support the use of a vSphere standard switch but implies downtime for the workload (The HCX team is working on adding support for the vSphere standard switch for other migration types). To minimize migration downtime, HCX has a single click option to extend on-premises networks (L2 stretch) to other on-premises sites or VMware Cloud on AWS. Once the workloads have been migrated there is also an option to migrate the extended network, if you choose. Other built-in functionality includes:</p>

<ul>
  <li>Native scheduler for migrations</li>
  <li>Per-VM EVC</li>
  <li>Upgrade VM Tools / Compatibility (hardware)</li>
  <li>Retain mac address</li>
  <li>Remove snapshots</li>
  <li>Force Unmount ISO images</li>
  <li>Bi-directional migration support</li>
</ul>

<p><img src="https://emadyounis.com/assets/img/2018/09/HCX-Migrations.png?resize=1280%2C800" alt="HCX Migration" title="HCX Migration" /></p>

<h2 id="summary">Summary</h2>

<p>HCX provides enhanced functionality on top of the built-in vSphere VM mobility options. Customers can now use HCX to migrate workloads seamlessly from on-premises to other paired on-premises sites (multisite) and VMware Cloud on AWS. Workload mobility can also help with hardware refreshes as well as upgrading from unsupported vSphere 5.x version. The next post will cover the different migration options available within HCX, followed by how to setup and configure the product.</p>]]></content><author><name>Emad Younis</name></author><category term="Hybrid Cloud Extension" /><category term="HCX" /><category term="Hybrid Cloud Extension" /><category term="NSX" /><category term="VMC" /><category term="VMware Cloud on AWS" /><summary type="html"><![CDATA[Hybrid Cloud Extension (HCX) is an all in one solution for workload mobility. Customers can freely move workloads between multiple on-premises environments as well as VMware Cloud on AWS (VMC). During the VMworld US 2018 day 1 keynote there were several demos shown, one included a data center evacuation using HCX (51:57). The data center evacuation was using a new HCX migration type called Cloud Motion with vSphere Replication. I’ll cover the HCX migration types in a later post. The workloads were being migrated from an on-premises data center to VMware Cloud on AWS (VMC). The big deal here is the impact during the migration to the users was NONE, ZIP, ZERO downtime. And there was also no replatforming of the workloads or applications.]]></summary><media:thumbnail xmlns:media="http://search.yahoo.com/mrss/" url="https://emadyounis.com/assets/img/2018/09/HCX-Blog-Feature-IMG.png" /><media:content medium="image" url="https://emadyounis.com/assets/img/2018/09/HCX-Blog-Feature-IMG.png" xmlns:media="http://search.yahoo.com/mrss/" /></entry><entry><title type="html">Stretched Clusters for VMware Cloud on AWS – Overview</title><link href="https://emadyounis.com/stretched-clusters-overview/" rel="alternate" type="text/html" title="Stretched Clusters for VMware Cloud on AWS – Overview" /><published>2018-05-14T12:30:39-07:00</published><updated>2018-05-14T12:30:39-07:00</updated><id>https://emadyounis.com/stretched-clusters-overview</id><content type="html" xml:base="https://emadyounis.com/stretched-clusters-overview/"><![CDATA[<p>VMware Cloud on AWS includes resiliency at different layers. We are all familiar with vSphere HA protecting against ESXi host failures. With VMware Cloud on AWS, ESXi hosts reside in an AWS availability zone and are protected by vSphere HA. What about protection for the availability zone the ESXi hosts reside in? While an AWS availability zone failure is a rare occurrence, customers should know they also are protected at this layer as well. A new feature called <a href="https://cloud.vmware.com/vmc-aws/roadmap">Stretched Clusters</a> for VMware Cloud on AWS is designed to protect against an AWS availability zone failure. Now applications can span multiple AWS availability zones within a VMware Cloud on AWS cluster. If an application instance fails the second instance in another availability zone can take over. This, of course, depends on if the application includes this level of availability. Let’s take a look at the Stretched Clusters feature.</p>

<h2 id="infrastructure-configuration">Infrastructure Configuration</h2>

<p>The Stretched Clusters feature deploys a single SDDC across two AWS availability zones. This option is only available during the SDDC creation steps under SDDC properties. When enabled the default number of ESXi hosts supported in a Stretched Cluster is six. Additional hosts can be added later but must to be done in pairs across AWS availability zones.</p>

<p><img src="https://emadyounis.com/assets/img/2018/05/Stretched-Cluster-SDDC-Properties.png?resize=1280%2C627" alt="Stretched Clusters for VMware Cloud on AWS" title="Stretched Clusters for VMware Cloud on AWS" /></p>

<p><img src="https://emadyounis.com/assets/img/2018/05/Stretched-Clusters-Number-of-Hosts.png?resize=1280%2C441" alt="Stretched Clusters for VMware Cloud on AWS - Additional Hosts" title="Stretched Clusters for VMware Cloud on AWS - Additional Hosts" /></p>

<p>The Stretched Clusters feature requires an AWS VPC with two subnets, one subnet per availability zone. The subnets determine an ESXi host placement between the two availability zones. As an SDDC is deploying, it provisions three hosts in each AWS availability zone and creates a vSAN stretch cluster across the two availability zones. The vSAN stretched cluster allows synchronous writes across the two availability zones. A vSAN witness node appliance, which looks like an ESXi host, will automatically be provisioned. It resides outside the SDDC cluster and in a third AWS availability zone. The vSAN witness node appliance is required in case network communication is lost, assisting to avoid split brain for virtual machines across AWS availability zones. Logical networks are also extended using NSX to support workload mobility across the two AWS availability zones.</p>

<h2><img src="https://emadyounis.com/assets/img/2018/05/Stretched-Clusters-Subnets.png?resize=1280%2C720" alt="Stretched Clusters for VMware Cloud on AWS - VPC and Subnets" title="Stretched Clusters for VMware Cloud on AWS - VPC and Subnets" /></h2>

<h2 id="workload-management">Workload Management</h2>

<p>Once a stretched clusters SDDC is available, go to the summary tab and view the VMware Cloud on AWS console. The console displays the capacity and usage of the SDDC for the two AWS availability zones.</p>

<p><img src="https://emadyounis.com/assets/img/2018/05/VMC-Console.png?resize=1680%2C584" alt="Stretched Clusters for VMware Cloud on AWS - vCenter View - VMC Console" title="Stretched Clusters for VMware Cloud on AWS - vCenter View - VMC Console" /></p>

<p>Now let’s login to vCenter Server. Here the SDDC will appear as a single logic datacenter with two fault domains. The ESXi hosts in the cluster span the two AWS availability zones. Customers can view which availability zone each host resides in from its summary tab. The fault domains listed correlate to the given AWS availability zone name. For a single view of all the ESXi hosts in a cluster and their fault domain, select the cluster and go to the Hosts tab. Within the Hosts tab, add the fault domain column.</p>

<p><img src="https://emadyounis.com/assets/img/2018/05/Stretched-Cluster-vCenter-Server.png?resize=1280%2C720" alt="Stretched Clusters for VMware Cloud on AWS - vCenter View" title="Stretched Clusters for VMware Cloud on AWS - vCenter View" /></p>

<p>When provisioning virtual machines, customers have options when deploying to an availability zone. The first option is auto placement. This occurs at the cluster level, where DRS will handle the placement of the workload. A more granular option is selecting a host in an availability zone to deploy virtual machines to. DRS will honor the virtual machine availability zone placement as a sticky rule. It will only move the virtual machine in case of a failure. vSphere HA will attempt to honor this placement decision if possible. An availability zone failure will have the same behavior as a vSphere HA event. All virtual machines in the failed availability zone will get restarted in another availability zone. vSphere HA restart priority is also taken into account:</p>

<ul>
  <li>vCenter Server has the highest restart priority. Other management virtual machines have a high restart priority</li>
  <li>Virtual machines migrated (cold or live) from on-premises will keep their restart priority</li>
  <li>New Virtual Machines created on a stretched cluster will restart after other higher priority virtual machines</li>
</ul>

<p><img src="https://emadyounis.com/assets/img/2018/05/VM-Provisioning.png?resize=1280%2C720" alt="Stretched Clusters for VMware Cloud on AWS - VM Deployment" title="Stretched Clusters for VMware Cloud on AWS - VM Deployment" /></p>

<p>Customers now have full resiliency for their mission-critical applications across AWS availability zones with zero RPO due to synchronous replication built in natively in their Cloud SDDC. You can use the VMware <a href="https://www.vmware.com/try-vmware/vmc-aws-hol-labs.html">Hands-On Labs</a> to test drive VMware Cloud on AWS and this new <a href="https://featurewalkthrough.vmware.com/t/vmware-cloud-on-aws/stretched-clusters/">product walkthrough</a> and <a href="https://www.youtube.com/watch?v=zea-hNiPois&amp;feature=youtu.be">video</a> to get familiar with the Stretched Clusters feature. <a href="https://twitter.com/glnsize">Glenn Sizemore</a> will also have a blog post coming with more details on the how storage works with Stretched Clusters, stay tuned.</p>]]></content><author><name>Emad Younis</name></author><category term="VMware Cloud on AWS" /><summary type="html"><![CDATA[VMware Cloud on AWS includes resiliency at different layers. We are all familiar with vSphere HA protecting against ESXi host failures. With VMware Cloud on AWS, ESXi hosts reside in an AWS availability zone and are protected by vSphere HA. What about protection for the availability zone the ESXi hosts reside in? While an AWS availability zone failure is a rare occurrence, customers should know they also are protected at this layer as well. A new feature called Stretched Clusters for VMware Cloud on AWS is designed to protect against an AWS availability zone failure. Now applications can span multiple AWS availability zones within a VMware Cloud on AWS cluster. If an application instance fails the second instance in another availability zone can take over. This, of course, depends on if the application includes this level of availability. Let’s take a look at the Stretched Clusters feature.]]></summary><media:thumbnail xmlns:media="http://search.yahoo.com/mrss/" url="https://emadyounis.com/assets/img/2018/05/Stretch-Clusters-for-VMWonAWS.png" /><media:content medium="image" url="https://emadyounis.com/assets/img/2018/05/Stretch-Clusters-for-VMWonAWS.png" xmlns:media="http://search.yahoo.com/mrss/" /></entry><entry><title type="html">vCenter Server Architecture Part 1 – The Basics</title><link href="https://emadyounis.com/vcenter-server-architecture-part-1-the-basics/" rel="alternate" type="text/html" title="vCenter Server Architecture Part 1 – The Basics" /><published>2018-05-07T14:07:18-07:00</published><updated>2018-05-07T14:07:18-07:00</updated><id>https://emadyounis.com/vcenter-server-architecture-part-1-the-basics</id><content type="html" xml:base="https://emadyounis.com/vcenter-server-architecture-part-1-the-basics/"><![CDATA[<p>With the release of <a href="http://emadyounis.com/vcenter/vcenter-server-6-7-whats-new-rundown/">vSphere 6.7</a> and 6.5 U2 comes architectural changes for vCenter Server. vCenter Server is going back to its roots of a simplified deployment model. vCenter Server used to be a single node deployment. The only debate was about its availability. Over time the architecture of vCenter Server has changed introducing a distributed deployment model. Core services like inventory, web client, SSO, and vCenter could run on separate nodes. vCenter Server had the potential of becoming six nodes in this model when adding the VCDB and VUM. The distributed deployment model became too complex for management, maintenance, and upgrades.</p>

<p>To simplify the distributed model, VMware introduced the Platform Services Controller (PSC). The role of the PSC is to manage authentication, licensing, tags &amp; categories, global permissions, and custom roles. It is also the certificate authority for the vSphere SSO domain. The PSC is a vCenter Server service which manages the components mentioned above. While the PSC is an improvement over the original SSO introduced in 5.1 and 5.5 it also added complexity. So began another debate of external versus embedded deployments. The reality comes down to enhanced linked mode. At the time (6.0 – 6.5 U1) only external deployments supported enhanced linked mode and external as a standalone. Now (6.5 U2 – 6.7) supports enhanced linked mode for embedded deployments. Now we are back to a more simplified deployment model and questions about how to transition.</p>

<p><img src="https://emadyounis.com/assets/img/2018/05/vCenter-Server-Deployment-Evolution.png?resize=1240%2C539" alt="" /><br />
Figure above represents the evolution of vCenter Server deployments. VMware has recognized the complexities involved in vCenter Server deployments and is putting efforts into getting back to a simpler deployment model allowing administrators can focus more on day-2 operations.</p>

<h2 id="psc-basics">PSC Basics</h2>

<p>Before we actually get into architecture it’s important to understand the basics. This is especially important when it comes to discussing availability. Let’s start with what happens when the PSC service is not available. We cannot authenticate (login) to vCenter Server, doesn’t matter if the PSC is embedded or external. Not only vCenter Server but other VMware products using the PSC for authentication will be affected. Examples are NSX, SRM, and vROPS to name a few. The next time you enter your credentials in the vSphere Client, hit enter, and watch the browser URL. You’ll see the URL change from vCenter Server’s FQDN to the PSC FQDN and back. For external deployments with several PSCs, it means losing a replication partner. This only affects authentication to any vCenter Server registered with the unavailable PSC. Workloads are still running, but the ability to login and centrally manage is not available. Now that you know the impact, think about who does this impact inside your organization. We’ll come back this during the availability discussion in this series.</p>

<p>It’s also important to understand the relationship between PSC and vCenter Server. An embedded PSC is only registered to the vCenter Server on the same node. An external PSC has a one-to-many relationship with vCenter Server.</p>

<ul>
  <li>vSphere 6.0 – a single external PSC can have up to 10 vCenter Servers registered</li>
  <li>vSphere 6.5 and 6.7 – a single external PSC can have up to 15 vCenter Servers registered</li>
  <li>vSphere 6.0 – supports up to 8 external PSCs within a vSphere SSO domain</li>
  <li>vSphere 6.5 and 6.7 – supports up to 10 external PSCs within a vSphere SSO domain</li>
</ul>

<p>One of the vSphere <a href="https://configmax.vmware.com/home">maximums</a> you don’t see is one for sites. A site is nothing more than a logic boundary and a way to group PSCs. You can have as many sites as you want as long as it does not exceed the number of supported PSCs in a vSphere SSO domain. Starting with vSphere 6.7 sites are not required for new deployments. During upgrades and migrations, sites will remain. Adding a new PSC to an upgraded or migrated environment will prompt for site information. External deployments can repoint vCenter Servers to any PSC in a vSphere SSO domain. Also now in vSphere 6.7 across different vSphere SSO domains. Currently, embedded deployments cannot repoint across different vSphere SSO domains. Sites are one less boundary to worry about going forward. The recommendation is to keep the default for new deployments from the GUI or CLI.</p>

<p><img src="https://emadyounis.com/assets/img/2018/05/Embedded-SSO.png?resize=1756%2C435" alt="vCenter Server embedded linked mode deployment" /><br />
<strong>Example 1</strong>: vSphere 6.7 embedded deployment with enhanced linked mode in a vSphere SSO domain. The PSC is running as a vCenter Server service in this example and everything within the vSphere SSO domain is considered a single default site.</p>

<p><img src="https://emadyounis.com/assets/img/2018/05/External-SSO.png?resize=1452%2C764" alt="vCenter Server external linked mode deployment" /><br />
<strong>Example 2:</strong> vSphere 6.7 external deployment with enhanced linked mode in a vSphere SSO domain. Everything within the vSphere SSO domain is considered a single default site.</p>

<p>The key thing to remember is the PSC is multi-master. Meaning there is no difference between the first one or the last one in the vSphere SSO domain. The PSCs replicate to each other every 30 seconds; this means if a PSC is unavailable the same data is available on its replication partners. To mitigate data loss, create a replication agreement between the bookends. This is referring to the first and last PSC in a vSphere SSO domain, creating a ring. The ring is creating a second data path in case you lose a data path. I’ve have seen several blog posts refer to the creating the ring as a requirement which is not true. The ring is a recommendation but not a requirement. Outside of the ring, creating more PSC replication agreements can cause unnecessary overhead. Keep it simple!</p>

<p><img src="https://emadyounis.com/assets/img/2018/05/Ring.png?resize=1447%2C895" alt="" /></p>

<p><strong>Example 3:</strong> An additional replication agreement created using vdcrepadmin from the last PSC to the first PSC (bookends) in the vSphere SSO domain, providing a secondary data path.</p>

<h2 id="vcenter-server-basics">vCenter Server Basics</h2>

<p>Most of the architecture discussions revolve around the vSphere SSO domain. There are some core concepts and considerations for vCenter Server as well. I pose the same question, but now what happens when the PSC is available but vCenter Server is not? The impact is you’ve lost management visibility and can not make any changes. Existing workloads are not affected by the outage. There are other implications to a vCenter Server outage. Some solutions communicating to vCenter Server as an endpoint will also lose access. For example, vROPS will not be able to collect metrics. Your backup window may also be affected. There are other products are resilient and not dependent on vCenter Server being available. Take vSAN for example, it is not dependent on vCenter and will continue to function. The VMware ecosystem has grown over the years and it’s important to know the impact of each solution within your environment when vCenter Server is not available.</p>

<p>We discussed the relationship between PSC to vCenter Server as one-to-many, but vCenter Server to PSC is 1:1. A vCenter Server can only be registered to a single PSC at a time.</p>

<ul>
  <li>vSphere 6.0 – supports 10 external vCenter Server deployments in enhanced linked mode</li>
  <li>vSphere 6.5 &amp; 6.7 – supports 15 external vCenter Server deployments in enhanced linked mode</li>
  <li>vSphere 6.7 – supports 15 embedded deployments in enhanced linked mode</li>
  <li>vSphere 6.5 U2 – supports 15 embedded deployments in enhanced linked mode</li>
</ul>

<p>In regards to physical location placement, VMware currently does not have any documented latency numbers. The recommendation is up to 100ms in a multisite configuration. This is the same for the new embedded with enhanced linked mode deployment. For external deployments at least one local PSC per site. Remember communication is continuous between vCenter Server and PSC. Stay tuned as we are trying to get official latency numbers published.</p>

<p>vCenter Server <a href="https://www.vmware.com/products/vsphere.html">licensing</a> comes up quite a bit. A standard vCenter Server license includes:</p>

<ul>
  <li>All PSCs when in an external deployment.</li>
  <li>Native vCenter Server high availability (VCHA)</li>
  <li>File-Based Backup / Restore</li>
  <li>Other advanced vCenter Server features</li>
</ul>

<p>vCenter Server also has a foundation version. It has limitations on available features and functionality compared to the standard version.</p>

<p>There are many questions about the new vCenter Server architecture 6.7, but I felt it was important to go basics. Over the next few posts, I’ll go into more details on both the embedded and external deployment models.</p>]]></content><author><name>Emad Younis</name></author><category term="vCenter" /><category term="Architecture" /><category term="vCenter Server 6.5" /><category term="vCenter Server 6.7" /><summary type="html"><![CDATA[With the release of vSphere 6.7 and 6.5 U2 comes architectural changes for vCenter Server. vCenter Server is going back to its roots of a simplified deployment model. vCenter Server used to be a single node deployment. The only debate was about its availability. Over time the architecture of vCenter Server has changed introducing a distributed deployment model. Core services like inventory, web client, SSO, and vCenter could run on separate nodes. vCenter Server had the potential of becoming six nodes in this model when adding the VCDB and VUM. The distributed deployment model became too complex for management, maintenance, and upgrades.]]></summary><media:thumbnail xmlns:media="http://search.yahoo.com/mrss/" url="https://emadyounis.com/assets/img/2018/05/Ring.png" /><media:content medium="image" url="https://emadyounis.com/assets/img/2018/05/Ring.png" xmlns:media="http://search.yahoo.com/mrss/" /></entry></feed>